How to Encrypt Environment Variables Securely
Learn how to encrypt environment variables, keep .env files out of Git, and load secrets safely in local development and CI/CD pipelines.
A plain-text .env file can expose the keys your app depends on, even if you never meant to share it. To encrypt environment variables safely, first sort secrets from ordinary settings, then encrypt and control how each secret reaches your app.
We analyzed 39 comments from YouTube and Reddit about encrypting environment variables and found that 36% mentioned particular encryption tools.
Step 1: Identify Which Environment Variables Need Encryption
Start with an inventory. An environment variable is a named value that a process can read while it runs. Some values are harmless settings. Others grant access.
Review each key and ask: if someone copied this value, could they access data, impersonate your app, or change a system? If yes, treat it as a secret. Database passwords, API tokens, signing keys, and private certificates belong in that group. A log level or a public service URL usually doesn't.
Make a simple inventory before you change files. Note each variable's purpose, owner, environment, and the app or pipeline stage that needs it. A key used only by a test job shouldn't be available to production deploys. Separate development, staging, and production values rather than reusing one credential everywhere.
- App settings: ports, feature flags, and log levels.
- Access secrets: passwords, API keys, tokens, and private keys.
- Public values: settings intended to appear in browser code or public docs.
Check less obvious places too. Search source files, test fixtures, build scripts, CI settings, logs, and container setup for credentials. A secret can leak through a debug print or a build artifact, even when the main .env file stays out of Git. Environment variables can also be inherited by child processes, so limit which jobs receive each value.
Where possible, use short-lived credentials scoped to one task. If a service needs a long-lived key, record who owns it and how to revoke it. That makes the next rotation a planned task, not a scramble after a leak.
For a shared setup, compare the workflow in our guide to encrypted environment variable manager subscriptions. EnvManager is built to encrypt, version, and manage .env files centrally, with role-based access and sync to local machines and CI/CD pipelines.
By now, you should have a list of secrets, their owners, and the jobs or people that need them.
Step 2: Choose an Encryption Method and Encrypt the .env File
Pick the method that fits where the file needs to go. Encryption turns readable data into ciphertext that needs a key to read. That only helps if the decryption key stays separate from the encrypted file.
For a small app, a local encryption tool can protect a file you need to commit or pass through a controlled workflow. Use the tool's documented commands to encrypt and decrypt the .env file.
Check the tool's current instructions before adopting a command in a shared script. Keep the encryption key in a separate secret store, not in the same repository as the ciphertext. If both land in Git, encryption has added steps without keeping the secret private.
Another option is a managed secrets service. A cloud secret store can hold values centrally and let an app or pipeline retrieve what it needs at runtime. Managed secrets services include AWS Secrets Manager, Azure Key Vault, and Google Secret Manager. A managed service can fit teams already using its cloud identity and access controls.
For shared .env workflows, EnvManager keeps encrypted files under central management and supports version control and role-based access. That can help when several developers need the same project values but shouldn't pass plaintext files through chat or email. Our comparison of encrypted .env backup and restore tools covers related choices for keeping a recoverable copy.
Whatever method you choose, test it with a harmless sample file first. Confirm that encryption produces a separate encrypted artifact. Then check that only an approved user or job can decrypt it. Keep the original plaintext file out of version control and remove extra copies from shared folders and build outputs.
Do not treat encryption as a fix for every exposure path. A decrypted file can still show up in a terminal, process log, crash dump, or backup. Avoid commands that print secret values. Make sure error messages name the missing variable without echoing its value.
By now, you should have an encrypted file or managed store, with its key held somewhere separate.
Step 3: Store and Share Encrypted Variables Safely
Keep ciphertext in the place your team needs it, and keep plaintext out of source control. Add local secret files to .gitignore. A basic setup might include:
.env
.env.local
.env.*.local
Then commit a .env.example file with variable names and safe placeholders. It tells a new developer what the app expects without handing over credentials. Check that ignore rules work: Git does not stop tracking a file that was already committed just because you added it to .gitignore later.
Don't share real .env contents through chat, email, or shared documents. Those copies can stick around in archives and search results. Give each teammate the access they need through a managed workflow. EnvManager lets teams manage .env files with role-based access, version control, and sync to local machines and CI/CD. Use those controls to keep production values away from people and jobs that only need development credentials.
Separate production secrets from preview builds and untrusted pull requests. If a job runs code from an outside contributor, don't expose production credentials to that run. Give each pipeline stage only the values it needs, and avoid printing the full process environment for debugging.
For cloud deployments, prefer a platform's secret store or a runtime secret service over copying a .env file into a container image or build artifact. If the app needs environment variables, load only its required values when the process starts. Public client-side variables are different: if a value is bundled into browser code, assume users can see it.
Keep separate credentials for local development and production. That way, a leak from a developer laptop doesn't hand out the same access used by a live service. When a teammate leaves or changes roles, update access rather than passing around a shared decryption key.
EnvManager can sync approved values to local machines and CI/CD pipelines, which can replace manual copy-paste as the handoff between developers and deploy jobs. If your main problem is getting encrypted files onto developer machines, our guide to syncing encrypted .env files locally looks at that workflow.
By now, the repo should hold only safe templates or ciphertext. Each person and job should get the values needed for its task.
Step 4: Decrypt at Runtime, Rotate Secrets, and Verify Access
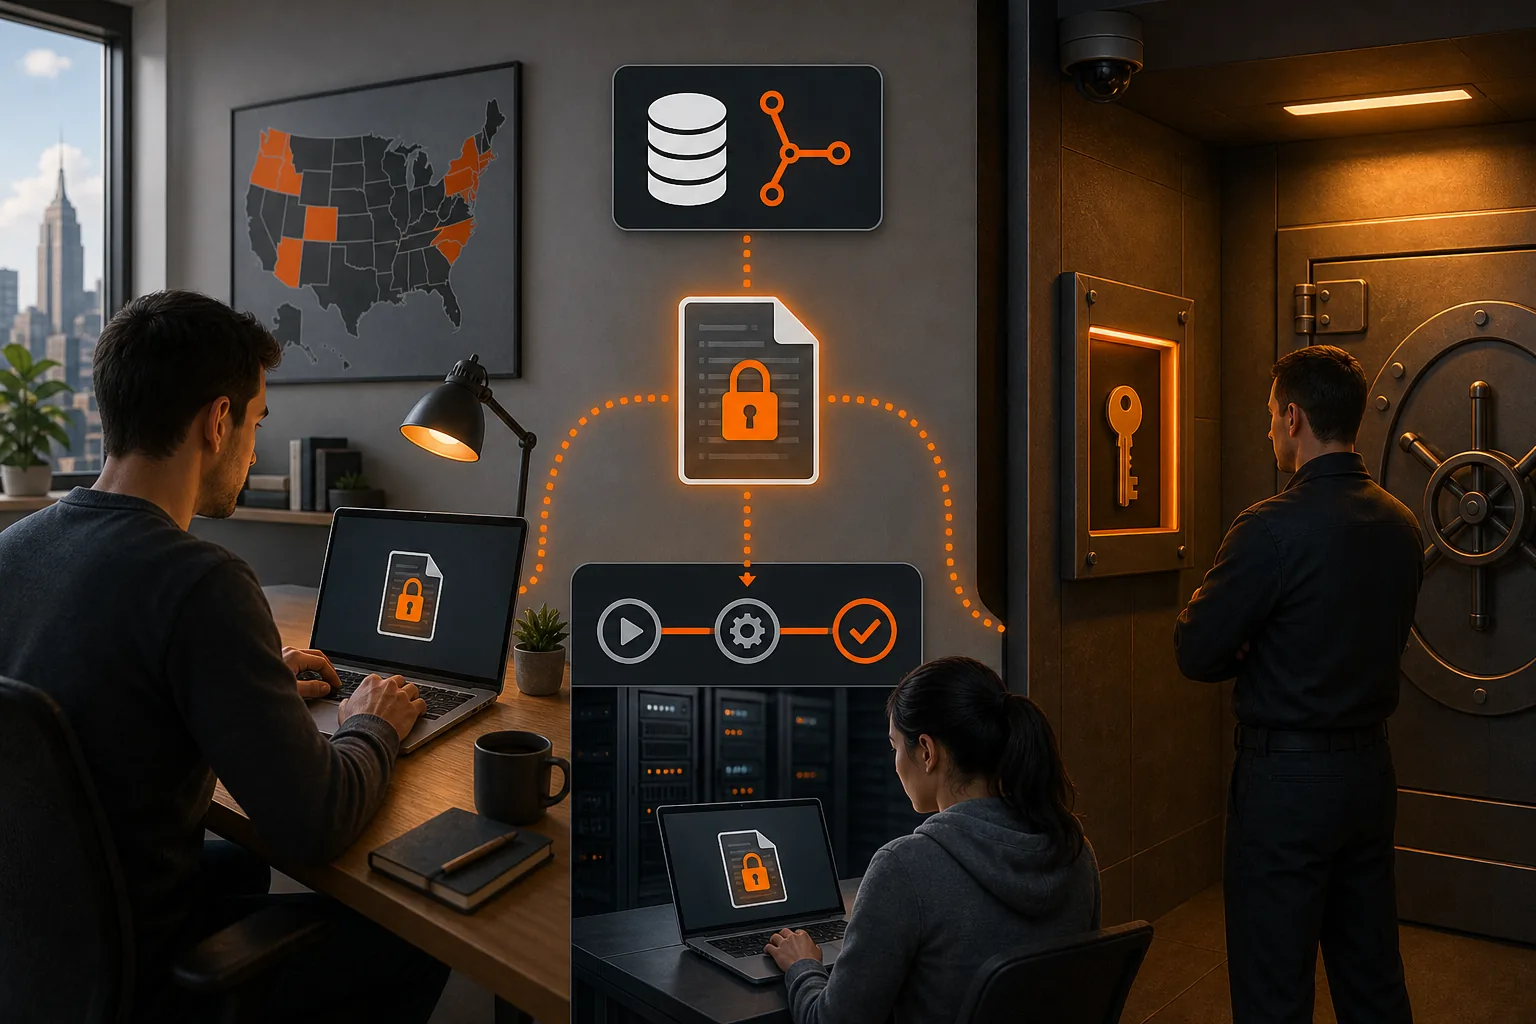
Decrypt as late as your app allows, and keep the plaintext available for as little time as the workflow permits. An application may need a secret in memory to use it. Encryption can't stop a process with permission to read that value from accessing it, so keep access narrow and avoid writing secrets to disk again.
For local work, use a command wrapper or approved tool to provide values to the process that needs them. With EnvManager, that looks like this:
envmanager run --only STRIPE_KEY -- npm run seedThe command requests one named value for one task instead of loading every project secret into the shell. Use the same principle in CI/CD: scope each secret to the stage that needs it, and make sure logs don't print command arguments or environment values.
Test the pipeline with a harmless sample secret before using production credentials. Confirm that the job can read the needed value, that a job without permission cannot, and that failure output doesn't reveal the secret. Decryption at startup adds work, but the actual delay depends on the tool, network, and app. Measure your own startup path instead of assuming the impact.
Set a rotation plan for credentials that can't expire automatically. Record an owner and revocation path for each one. When a key is exposed, revoke it at the service that issued it, create a replacement, and update every approved consumer. Removing the value from a current file won't erase it from Git history or invalidate the credential.
For a planned rotation, update the secret store first, then deploy the app or job that uses the new value. Verify the service works before retiring the old credential. If the provider supports short-lived credentials, consider using them instead of long-lived static keys.
Finally, review access and change records on a set schedule. EnvManager includes version control, role-based access and an immutable audit trail for secret changes. An audit record helps a team trace edits during a review, while access rules limit who can make them. Keep the review tied to actual owners and environments, not just a checkbox in a process document.
By now, you should have a working load path, a tested permission boundary, and a repeatable plan to rotate or revoke credentials.
FAQ
Should I encrypt a .env file before committing it?
Encrypt a .env file before committing it only if the decryption key is stored separately and access is limited. A safer default is to keep plaintext .env files out of Git and commit a placeholder-only .env.example. If your team needs encrypted files in version control, test who can decrypt them and check that keys never enter the same repository.
Are environment variables encrypted by default?
No, environment variables are not automatically encrypted just because they're stored outside your source code. A process can read values it receives, and logs or child processes can expose them. Use a secret store or encrypted file workflow to protect storage and delivery, then limit which jobs and users can access each value.
Can I decrypt secrets directly in a CI/CD pipeline?
Yes, a pipeline can decrypt or retrieve secrets at run time, as long as its key access is restricted. Give each job only the credentials it needs. Keep values out of logs and artifacts, and test the workflow with a harmless secret before connecting production credentials.
How often should I rotate environment variable secrets?
Rotate secrets based on the service's rules and your team's risk policy; there isn't one interval that fits every credential. Revoke and replace a key right away if it may have leaked. For keys that remain active, assign an owner and document how to replace the value in every app and pipeline that uses it.
Conclusion
Keep plaintext .env files out of Git, separate encryption keys from ciphertext, and grant each person or job only the access it needs. Start by inventorying one project, then encrypt or move its highest-risk secrets and test the full load and rotation path. EnvManager can manage shared .env values across local work and CI/CD when your team needs a central workflow.