Access Governance Software: A Setup Guide
Learn how to set up access governance software, define roles, automate access changes, and run reviews that keep permissions aligned with each person's job.
Access reviews get messy when permissions live in separate apps, old accounts linger, and no one can say who approved a change. Access governance software helps you set rules for who gets access, why they get it, and when it should end. Use these steps to build a system that fits your environment, then add focused controls for developer secrets where you need them.
We analyzed 25 Reddit comments about access governance software and found that 24% mentioned a unified SaaS lifecycle platform.
Step 1: Inventory Users, Applications, and Access
Start with a clear map of identities and permissions. Access management handles the day-to-day work of granting or removing access. Governance adds the rules and checks that help decide if that access is still right.
List the people and systems that hold identities: employees, contractors, service accounts, and automated agents. Then record each application or data store they can reach, the account or role they use, and who owns that access. Include cloud services, on-prem systems, and SaaS apps. A list limited to your main identity provider can miss accounts created directly in other tools.
Pull identity data from the sources that best reflect the truth in your company. That may include HR records, identity platforms, directories, and app-level user lists. Check how each system matches accounts to people. Two accounts with similar names can belong to different people, while one worker may appear under different names across systems.
For each permission, note what it allows in plain language. “FIN_APPR_2” tells a manager little. “Can approve vendor payments” gives them something useful to review. Mark accounts with broad privileges, no active owner, or no clear business purpose for follow-up.
Use the inventory to set a baseline, not to claim that every account is already correct. A review tool can only show what its connected sources provide. Teams weighing broader identity needs can compare identity governance and administration tools against their systems and review workload.
Keep developer secrets in scope too, but treat them as a distinct access problem. EnvManager manages encrypted, version-controlled .env files with role-based access, then syncs approved secrets to local machines and CI/CD pipelines. It can help govern access to application secrets, while broader workforce governance still needs to cover accounts across your other systems.
By now you should have an account and application inventory with an owner, access level, and source for each entry.
Step 2: Define Roles, Policies, and Approval Rules
Turn the inventory into rules people can apply. A role groups permissions around a job or task. A policy sets the limits for assigning those permissions, including who can approve them and when access should be reviewed.
Begin with a small set of real job functions. For example, a payroll specialist may need access to payroll records but not the right to change identity settings. A production engineer may need deployment secrets for one service, not every project’s credentials. Give each role only the permissions needed for its work, then name an owner who can explain why those permissions belong together.
Write policies for the cases that create risk or confusion. Set rules for privileged access, external workers, temporary access, and sensitive data. Define conflicting duties too. A person who can create a vendor and approve that vendor’s payment may need a second check. Test each rule with a sample identity before applying it broadly. If the policy depends on a role assignment, test that role directly rather than assuming an underlying permission will trigger the rule.
Approval rules should reflect the risk. A low-risk request may need a manager’s approval. A sensitive data role may need both the manager and the resource owner. Set a clear path for exceptions, plus an end date for temporary access.
Make the policy readable by the people who use it. State the role’s purpose, the resources it covers, and what it cannot do. Avoid role names that only make sense to the team that built them. If two roles grant nearly the same access, decide whether to combine them or document the difference.
Entitlements are the individual rights inside a role or access package. Map those rights to job tasks before setting approval rules. This is also where entitlement management software can help frame how access rights are grouped and controlled.
By now you should have named roles, written policy rules, and tested approval paths for routine and high-risk requests.
Step 3: Configure Access Requests and Provisioning
Give people a clear way to ask for access, and make sure approved requests reach the right system. A request should state the resource, the level of access, the business reason, and the requested duration. The requester should be able to see whether it is waiting, approved, or denied.
Build request options around roles or access bundles when possible. That’s easier to review than asking people to choose from a long list of raw permissions. Add a free-text reason only as supporting context. It should not replace the actual access scope or an end date.
Route each request to the person who can judge it. A manager can confirm that the request fits the person’s job. A resource owner can check the impact on an application or data set. For sensitive access, require both. Requests can go through preset approvers and then trigger provisioning after a decision.
An approval workflow can let an approver approve, reject, or request more information. After approval, the workflow can trigger provisioning in the connected system. Use that pattern to avoid treating approval as the finish line.
Connect the workflow to the system that grants access. Confirm that the connector can create the account or assign the permission you expect. Test a request from start to finish, including a rejection and an expired request. Then check the target application itself to make sure the change took effect.
Set safeguards for requests that fail or stall. Name an owner for connector errors, and make sure the requester or approver can see when action is needed. For production secrets, keep the scope narrow and the approval path explicit. EnvManager can manage .env values centrally with role-based access and sync them to development workflows; use it for secrets governance rather than as a substitute for organization-wide identity approvals.
By now you should have a request flow that records the reason, decision, and provisioning result.
Step 4: Automate Joiner, Mover, and Leaver Access Changes
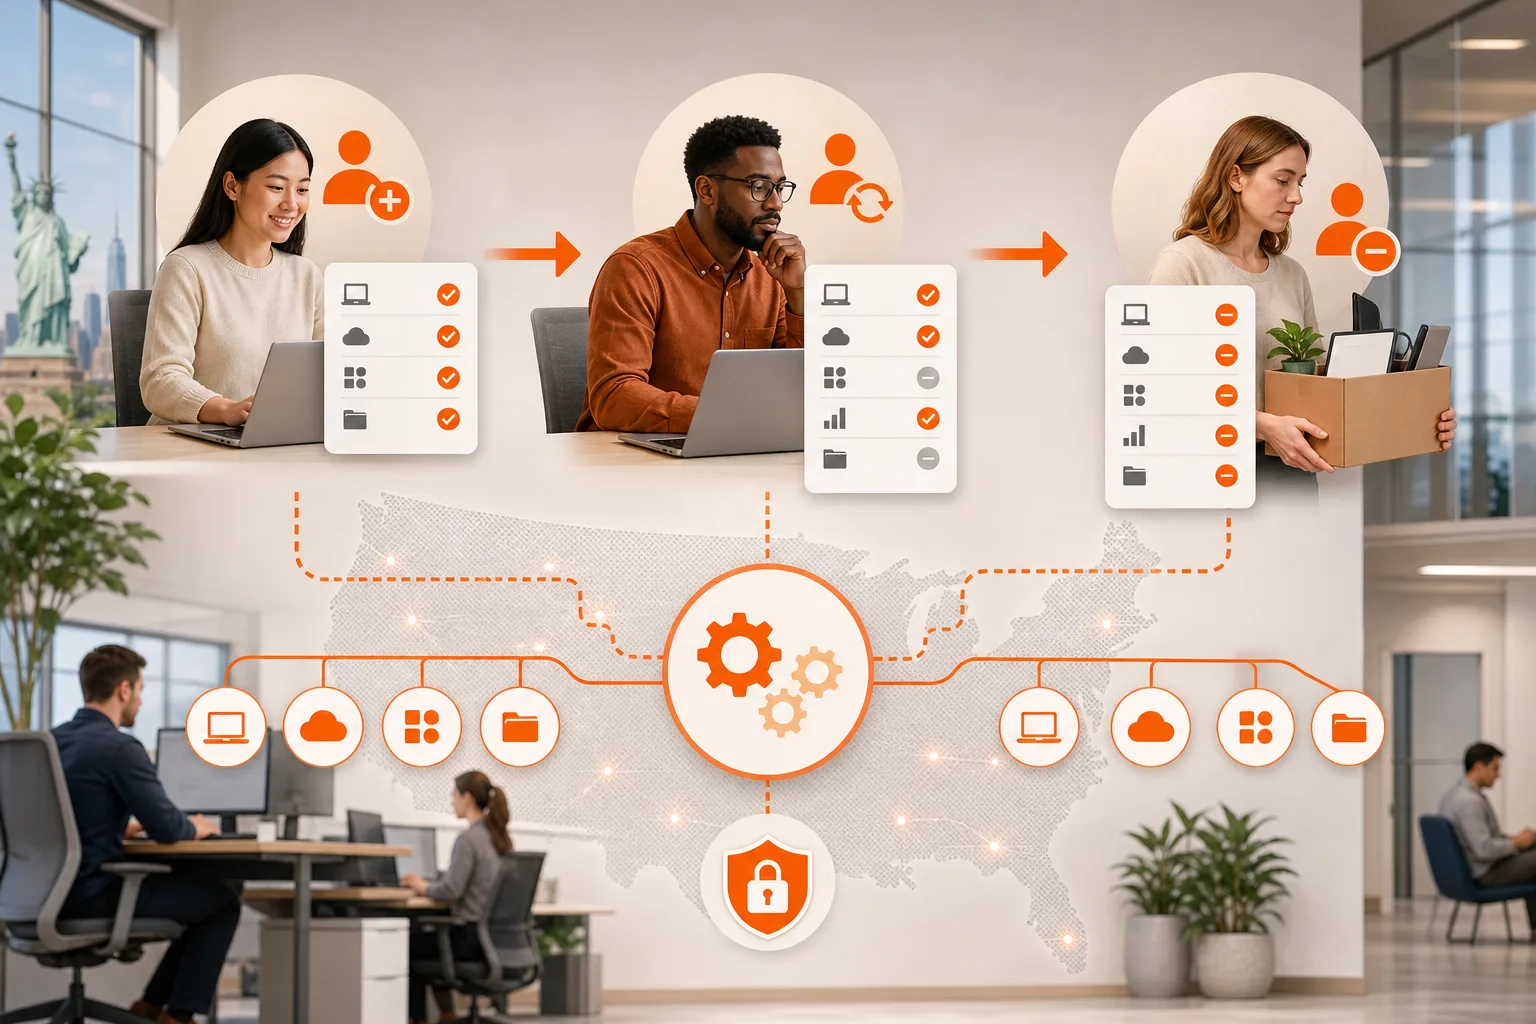
Connect identity changes to access changes. When someone joins, moves to a new role, or leaves, their permissions should follow the approved rules instead of relying on a manual reminder.
Choose the authoritative source for each identity event. HR data often signals a hire, department change, or termination. Your identity system may then pass that change to connected apps. Map job attributes such as department or worker status to the roles and permissions they control. Start with one team or application group, then verify the results before adding more.
For new workers, define the access they need on day one. Keep default access limited to the tools required for onboarding and the person’s role. For a role change, add the new permissions and decide which old ones must end. Removing access that no longer fits is as important as granting the new role.
For departures, set a clear trigger and confirm the target systems disable or remove the account. Don’t assume that changing a record in the source system has removed access everywhere. Check the result in the application, especially for accounts that use a separate login or are not connected to central provisioning.
Plan for exceptions. A delayed start date, leave of absence, or temporary project assignment may need a different rule. Give each exception an owner and an end date. Also define what happens when a provisioning task fails. A visible failed status and a named responder beat a silent error that leaves old access in place.
Apply lifecycle rules to non-human identities too. Service accounts need an owner and a business purpose, even when no employee signs in with them. When a service or integration is retired, remove its account or transfer ownership through a recorded process.
By now you should have tested joiner, mover, and leaver events against connected systems, including the path for exceptions and failed actions.
Step 5: Run Access Reviews and Maintain Audit Evidence
Review access on a set schedule and after major changes. An access review asks whether each person still needs the permissions they hold. It is one part of governance, not the whole program. The wider cycle also covers how access is requested, approved, granted, changed, and removed.
Choose the review owner based on the access. Managers can check whether permissions fit a person’s role. Application or data owners can judge whether a specific entitlement is still needed. Set a scope that reviewers can finish, and give them enough context to make a decision. Show what the permission does, when it was granted, and who owns the resource.
Ask reviewers to approve, revoke, or send an item for follow-up. Require a reason for revoking access or approving a high-risk exception. Then track remediation until the target system reflects the decision. A completed review without a completed change leaves the original exposure in place.
Record the campaign scope, reviewers, decisions, timestamps, exceptions, and remediation status. Keep the evidence in a place your security or audit team can retrieve. Test an export before a formal review, so you know it includes enough detail to explain what happened and when.
Use risk signals to focus reviewer attention, not to make decisions on autopilot. A rarely used permission or an unusual combination of roles may deserve a closer look. Automation can sort and flag items, but a qualified owner should decide whether access matches the person’s work.
For development teams, secret access needs its own evidence trail. EnvManager centralizes .env file management with role-based access and version control, helping teams track changes to development secrets. Keep this evidence connected to the relevant project and review process. This guide to user access review software can help you compare review workflows across connected systems.
By now you should have a repeatable review cycle and evidence that links each decision to its follow-up action.
FAQ
What does access governance software do?
Access governance software helps an organization decide who should have access, what they can do, and when that access should end. It supports policies, approval workflows, access reviews, and evidence of decisions. Access management handles the mechanics of granting or removing access; governance checks whether those permissions remain appropriate.
How is access governance different from identity management?
Identity management handles identity records and common account tasks, such as creating or updating a user. Access governance adds rules for assigning permissions and checking whether they still fit. In practice, the two work together: a job change updates identity data, then governance rules guide which access should be added or removed.
How often should we review user access?
Set a review schedule that matches the sensitivity of the access and your internal control needs. Review high-risk permissions more often than routine access, and trigger a review after events such as a job change or departure. Assign an owner and track each removal to completion rather than counting a submitted review as finished.
Can EnvManager replace an enterprise identity governance system?
No. EnvManager manages encrypted, version-controlled .env files with role-based access and syncs secrets to local machines and CI/CD pipelines. That makes it relevant to development secret access. It does not replace governance for workforce identities and permissions across an organization’s wider application estate.
Conclusion
Start with an accurate inventory, then build policies around actual job needs and verify that approved changes reach the target systems. Use access governance software for organization-wide identity decisions, and use EnvManager when your development team needs tighter control over .env secrets. Pick one application and test the full request-to-review cycle before expanding the rollout.