Developer Security Tools: How to Build a Secure Workflow
Put developer security tools to work by mapping risks, protecting secrets, adding CI/CD checks, and testing access, rotation, and recovery.
Leaked keys and shared .env files turn small workflow gaps into access risks. Developer security tools help close those gaps when they fit the way your team builds and ships software. Start by mapping where secrets move, then add controls at the points where they can leak.
Step 1: Map Your Development Workflow and Identify Risks
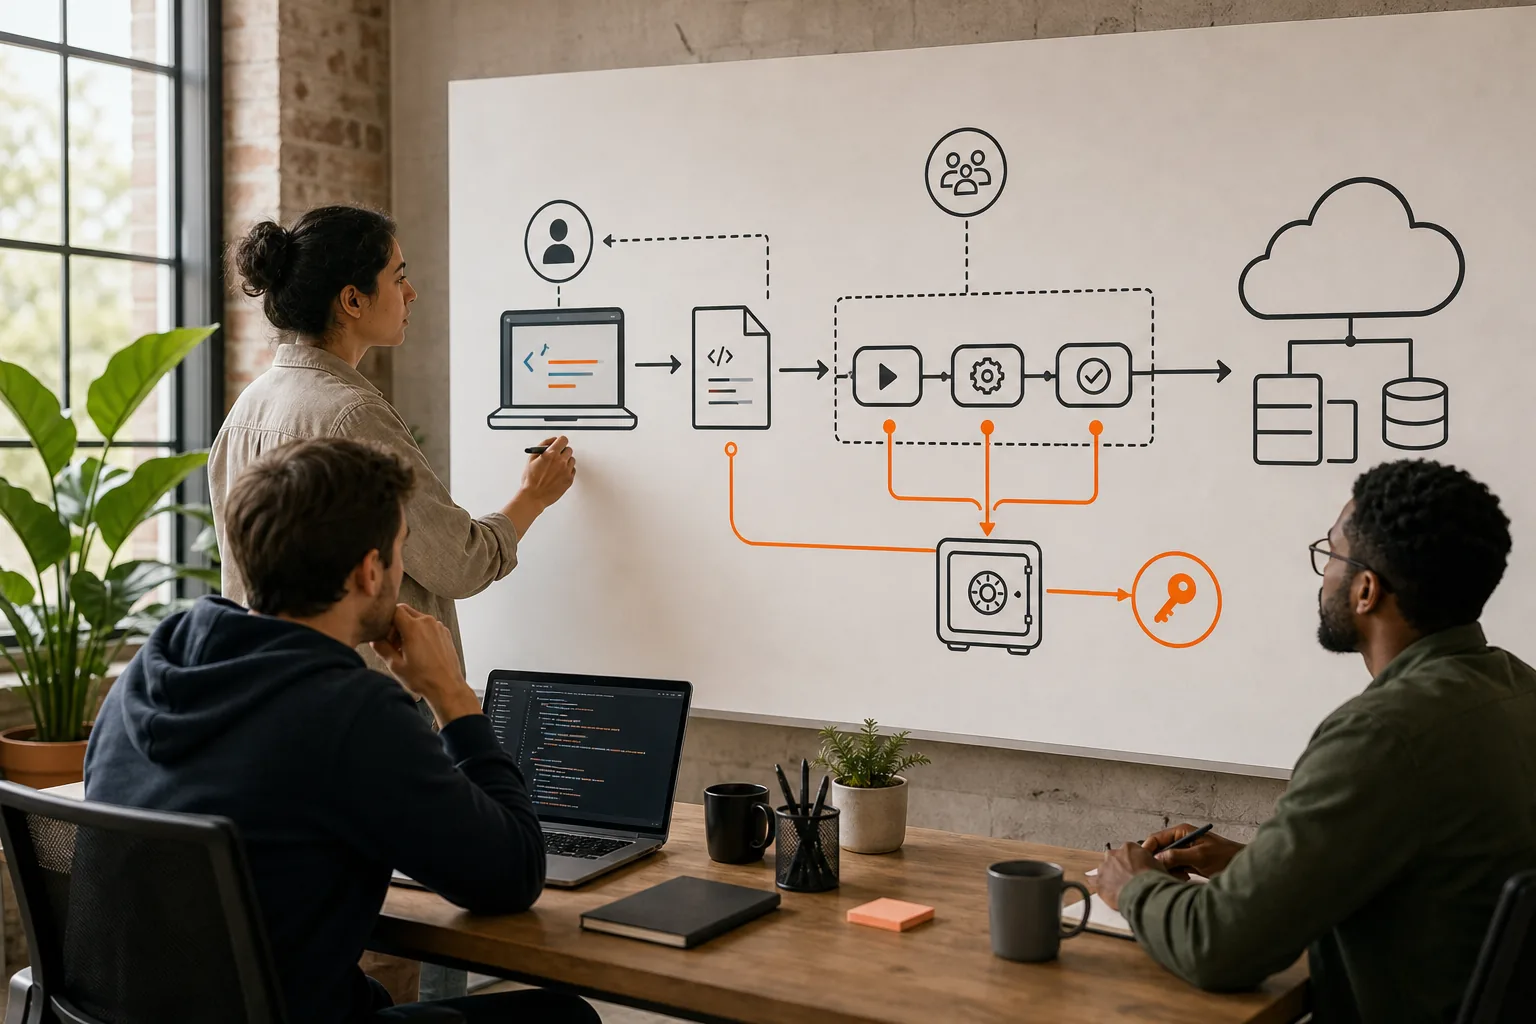
First, trace one change from a developer’s laptop to production. Write down where code lives, where builds run, which services receive credentials, and who can change each setting. Include local development, test environments, production, and any shared deployment tools.
Then mark each place a secret could land. Check source code, pull requests, build logs, local .env files, CI settings, and deployment dashboards. A key copied into a repository can remain in its history even after someone removes it. A shared production credential also makes it hard to tell whose action changed a service.
Keep the map tied to a real app. For example, a developer may need a payment key for a local seed task, while a deployment job needs a different credential. If both use the same production key, a mistake in local work can have production impact. List the owner and purpose of every credential before choosing controls.
Make an inventory of repositories, runners, deployment targets, and the people or services that can reach them. Teams with a wider device or network scope may also find a guide to network asset discovery tools useful when deciding which connected assets belong in the security map.
For code-level checks, match the risks you find to the right scan type. Consider code security scanning tools as part of that process.
Milestone: You should have a simple flow map that shows each secret’s source, destination, owner, and use.
Step 2: Match Security Tools to the Risks You Found
Choose controls for the gaps on your map, not by counting features on a sales page. A secret manager stores and shares credentials. A code scanner checks source for risky patterns. Dependency checks look for known issues in outside packages. Infrastructure checks review configuration before it reaches cloud systems.
These jobs overlap, but they are not the same. A scanner can flag a key in a commit; it cannot replace the key or set permissions for the new one. A secrets manager can limit access to a credential; it does not prove that application code is safe. Assign each risk to a control and name the person who will act on a finding.
For local .env files and team access, EnvManager is built to encrypt, version-control, and centrally manage environment files, with role-based access. It can sync secrets to developer machines and CI/CD pipelines. It has one flat team price and a seven-day trial without a credit card, which can make it easier to test the workflow before adopting it.
For broader infrastructure needs, compare the job each system handles. AWS Secrets Manager supports automatic credential rotation and records access through AWS CloudTrail. Google Cloud Secret Manager includes user-level access policies. Those may suit cloud-specific needs, while an .env-focused workflow may call for a different fit.
Be careful with vague feature claims. Ask vendors to show how a secret is encrypted, how access is limited, what the audit record captures, and how a pipeline retrieves values. The phrase “supports rotation” needs a clear explanation of what rotates, when it happens, and what happens if the update fails.
The right mix can include more than one control. Keep ownership clear so a finding does not sit between teams.
Step 3: Centralize Secrets and Set Least-Privilege Access
Move shared credentials out of chat, source control, and hand-maintained copies. Put each secret in a managed store, then give access only to the people or services that need it. Role-based access control, or RBAC, lets you grant access by job instead of sharing one broad credential with a whole team.
Start with separate scopes for development, staging, and production. A local test should not inherit a production payment key just because both environments use the same variable name. Keep access tied to a project or service, and review it when someone changes teams or leaves.
EnvManager centrally manages and version-controls .env files, then syncs them to local machines and CI/CD workflows. That gives your team one controlled source for environment values instead of a chain of manual copies. A version history also helps you see which configuration changed when a deployment starts failing.
For a command that needs a secret briefly, use an execution pattern that injects it for the task rather than putting its value in the command text. With EnvManager, that looks like this:
envmanager run --only STRIPE_KEY -- npm run seedThat keeps the secret value out of the command you type. Still, review shell history, process output, and CI logs as part of your setup. A well-managed secret can leak if a script prints its environment or stores it in a build artifact.
Some tools retrieve secrets just in time, meaning a process gets a value when it needs it rather than keeping a long-lived copy. Choose a method that fits your app and does not force developers to paste values by hand.
Milestone: Each secret should have a named owner, a narrow access scope, and a clear path into the task that needs it.
Step 4: Integrate Security Checks Into Local and CI/CD Workflows
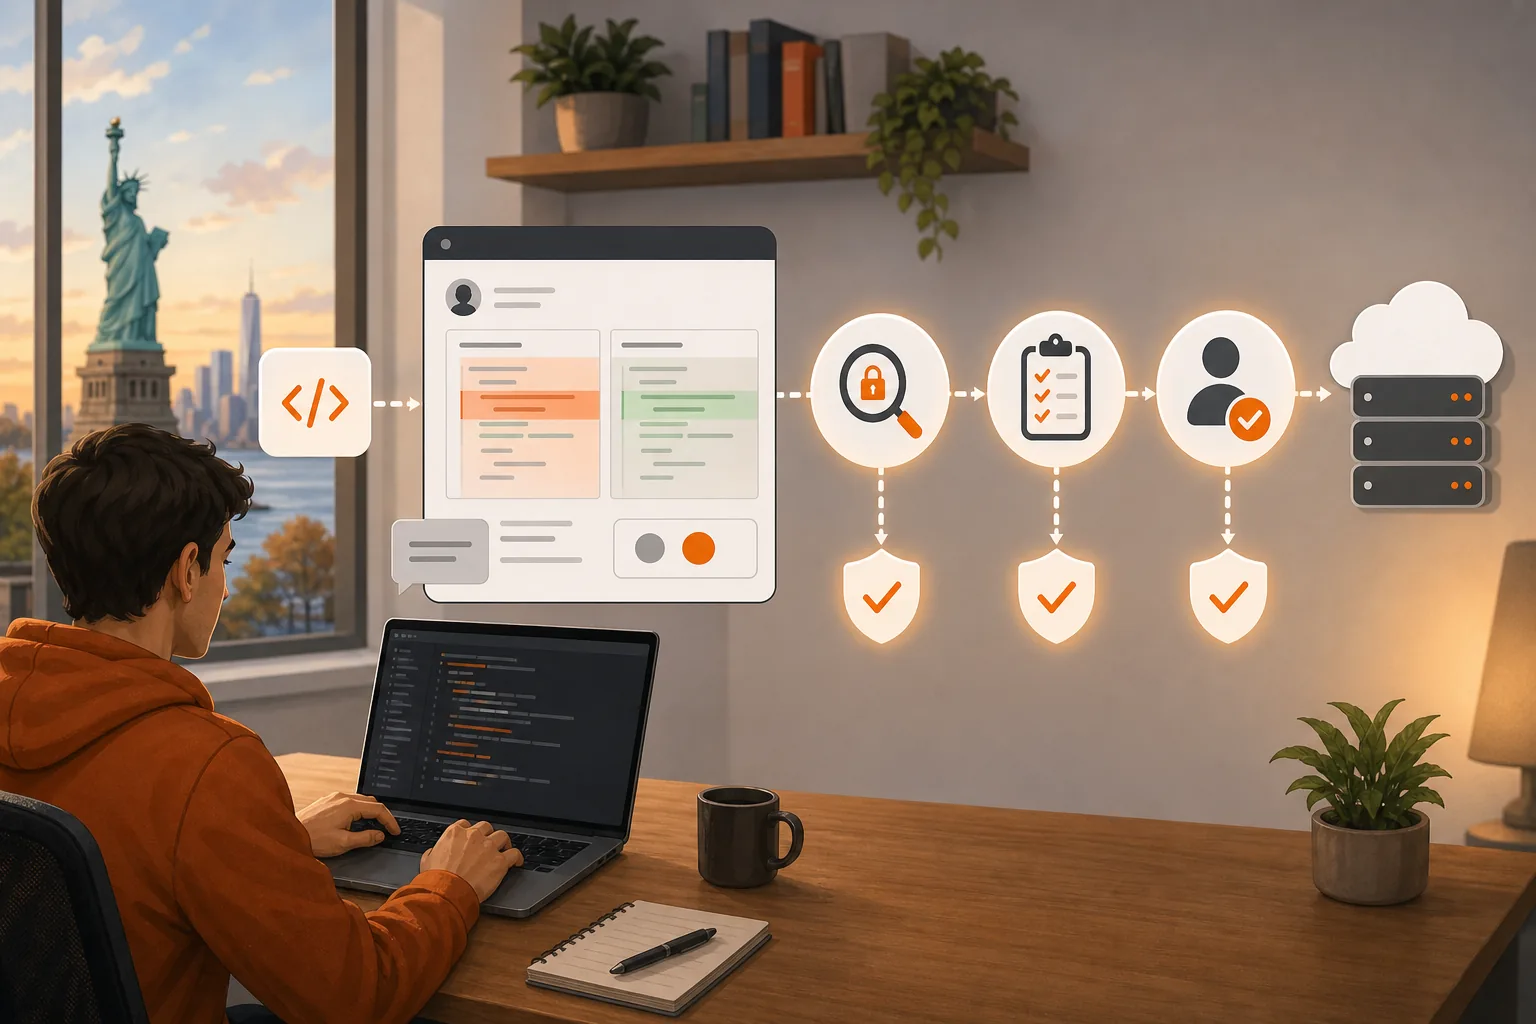
Run fast checks close to the work, then add deeper checks at build or release time. A local pre-commit scan can catch an accidental credential before it enters a repository. A pipeline can check code and dependencies when a change is pushed. Infrastructure checks can flag unsafe settings before deployment.
Keep each check focused. Secret scanning looks for exposed credentials. Static application security testing tools review code without running it. Dependency checks inspect packages your app uses. Dynamic tests examine a running service, which can reveal issues that a source-only check misses.
Set the first pipeline version to report findings without blocking every build. Review what it catches and who owns each type of issue. Then add blocking rules for clear, high-risk cases. If every noisy warning stops a release, developers may learn to bypass the check instead of fixing the cause.
Also protect the pipeline itself. Limit who can edit workflows, review third-party actions before use, and keep runner permissions narrow. Secret scanning can help catch credentials committed to source control.
If your service depends on APIs, include tests in the same release path, alongside secret controls and code review. Free API integration testing tools may help when considering testing options.
EnvManager can sync environment values to CI/CD pipelines, so teams can reduce manual transfers between local work and deployment settings. Decide which secrets a job needs, then configure the narrowest access that lets it complete.
Milestone: A code change should trigger the checks that fit its risks, with an owner for every blocking finding.
Step 5: Verify Rotation, Audit Logs, and Recovery Procedures
A security control is only useful if your team knows how to use it during a real change or incident. Test the full path: update a credential, make sure the intended service receives it, and confirm the old value stops working where appropriate. Don’t assume a rotation setting worked just because a screen says it is enabled.
Write down which credentials rotate automatically and which need a person to act. For each one, record the owner, the system that uses it, the steps to update it, and the way to verify the change. AWS Secrets Manager, for example, supports automatic rotation for credentials. Confirm that any rotation process fits the service that depends on the secret.
Review audit records on a schedule. Check who accessed or changed a secret, when the action happened, and whether it matches a planned task. An immutable audit trail is a record designed to resist alteration. It can help your team reconstruct a change during an incident, but only if the right events are captured and someone knows how to review them.
Practice a leak response before you need one. Revoke the exposed key, issue a replacement, update the services that use it, and check logs for unexpected access. Then remove the leaked value from current files and assess its repository history. Deleting a line from the latest version does not erase earlier commits.
Keep a recovery path for a failed rotation or lost access. Name who can restore service, how they confirm the replacement works, and where the record of the incident lives. Test this in a non-production environment first. The point is to make recovery a known task, not an improvised scramble.
EnvManager’s version-controlled environment files can help teams track configuration changes. Pair that history with a clear credential replacement process, since a change record alone does not rotate a secret.
Finish by running one drill: pick a test credential, rotate it, review the access record, and document what you learned.
FAQ
What are developer security tools?
Developer security tools are software that helps teams find or reduce risks during software development and delivery. The set can include code scanners, dependency checks, secret managers, infrastructure checks, and pipeline controls. Pick tools based on the risks in your workflow, then connect each finding to an owner and a fix.
Which security tool should a development team add first?
Start with the control that closes your clearest risk. If secrets sit in shared files or CI settings, centralize them and limit access. If exposed keys or risky code are reaching repositories, add secret scanning or code checks. Map the workflow first so the new tool addresses a real gap.
How do I keep secrets out of source control?
Store secrets outside the repository and pass them to local tasks or CI jobs through a managed secret workflow. Add secret scanning before commits and in the pipeline, and ensure .env files with sensitive values are excluded from version control. If a key leaks, revoke it and replace it; deleting the visible line is not enough.
Do developer security tools replace code review?
No. Automated checks can flag known patterns or configuration issues, but people still need to review whether a change makes sense in context. Use tools to catch repeatable problems early. Keep code review for design choices, permissions, and findings that need human judgment.
Conclusion
Map how a secret moves before you add another scanner or dashboard. Then choose controls that fit those paths, keep access narrow, and test your response to a leaked key. If your team needs centralized .env management, try EnvManager’s seven-day trial and start by moving one development workflow into it.