How to Set Up Temporary Scoped Secret Access
Set up temporary scoped secret access with least-privilege rules, short-lived credentials, secure delivery, and a clear revocation and audit plan.
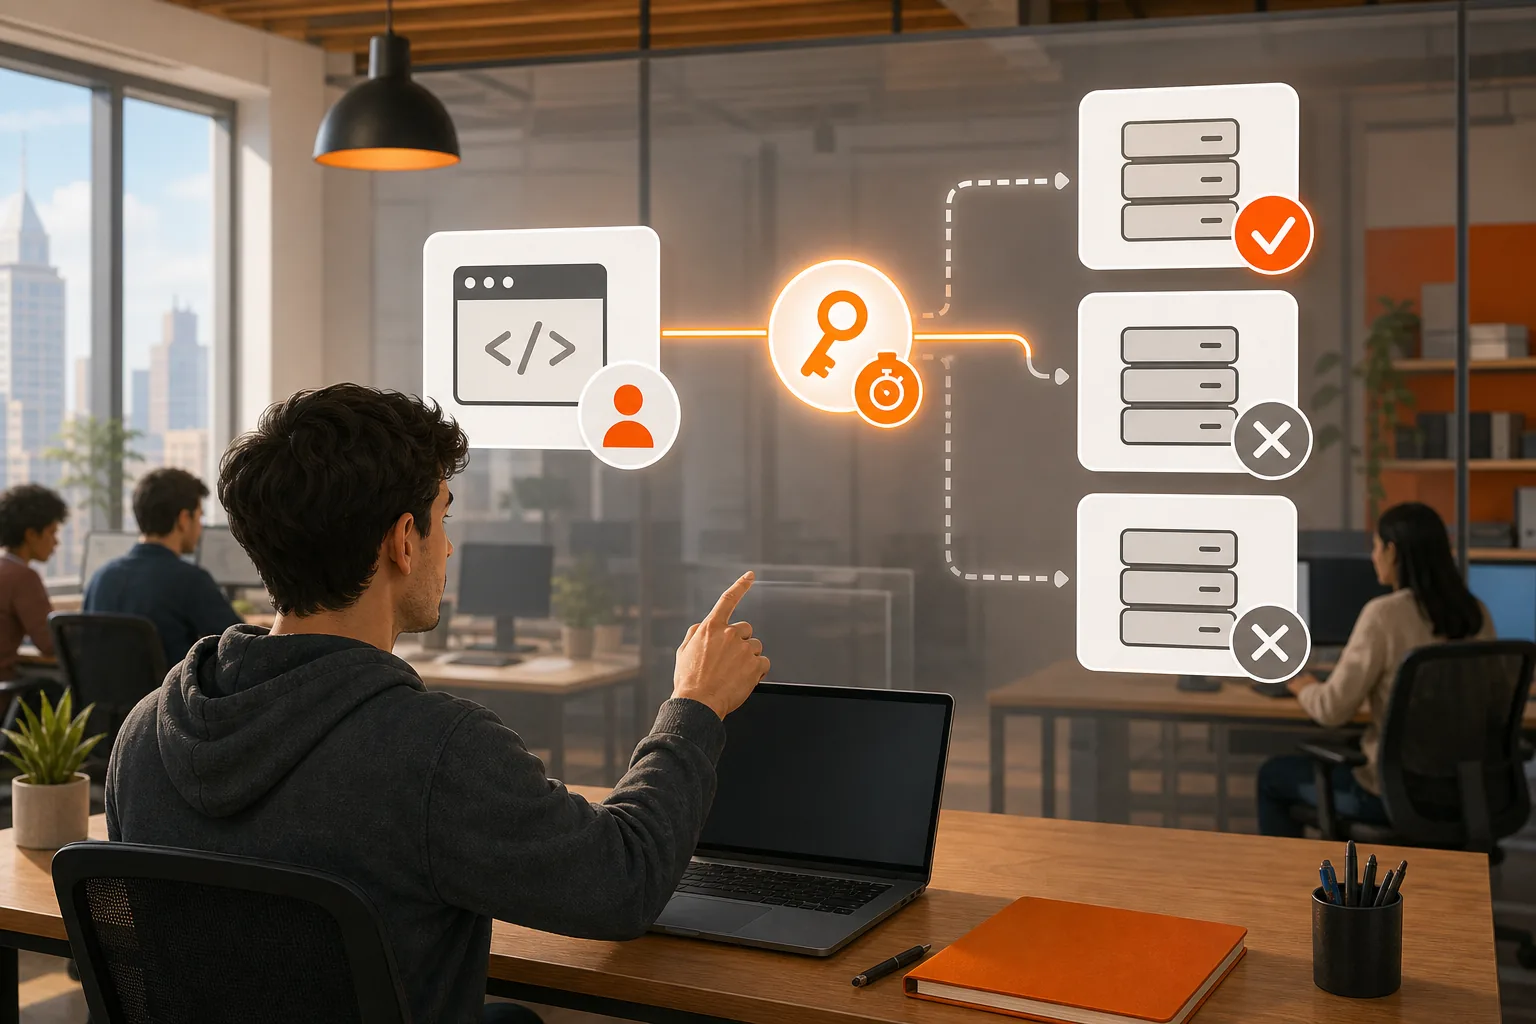
A permanent key can outlive the task it was made for. To set up temporary scoped secret access, give each person or job only the permissions it needs, then make access expire or end with the task.
We analyzed 33 comments and questions from Reddit, Quora and YouTube about temporary scoped secret access and found that 24% mentioned short-lived least-privilege credentials.
The steps below cover local commands, cloud roles, and CI/CD identity. The same rule applies to all of them: prove what should work, then prove what must fail.
Step 1: Define the Secret, Scope, and Expiration
Start by naming the exact secret and task. “The deploy job needs the production payment key to run a release” is useful. “The pipeline needs production access” is too broad.
Write down four limits before you grant anything:
- Identity: Which developer, service, or workflow needs access?
- Resource: Which project, environment, secret, or cloud role is in scope?
- Action: Does the task need read access, or must it also change data?
- Time: When should access expire, and can it end sooner when the task finishes?
Scope can mean different things. A per-secret grant is narrower than a project-wide grant. A per-job credential can end with one workflow run. For development secrets, EnvManager uses project and environment roles, while its CLI can inject selected values into a single command. That keeps a local shell from becoming the place where every secret lives.
Separate production from staging at this point, not after rollout. If a staging test can use a production key, the scope is not doing its job. The per-environment access control approach for .env files can help you define that boundary before assigning roles.
Pick an expiration that matches the work. A one-off database fix may need a short window. A deployment credential should usually last only for the job or session, when the platform supports that model. Don't assume a default token lifetime: set it explicitly and check the issued credential.
Milestone: You should have a named identity, resource, action, and end time. If any one is vague, narrow the request before moving on.
Step 2: Choose a Short-Lived Credential Method
Choose the way access will be issued based on who or what needs the secret. A person using a cloud console may assume a temporary role. A CI job can prove its identity through OpenID Connect, or OIDC, and request credentials for that run. A local command can inject only selected values into the process it starts.
Think of an OAuth access token like a hotel key card. The token proves a limited right to act; it is not the user's main password. Its issuer, audience, permissions, and expiry still need checks. A token with a broad scope or long lifetime can create much the same risk as a static key.
For AWS access, the Security Token Service, or STS, can issue temporary credentials when a trusted identity assumes a role. This fits console sessions, CI/CD jobs, and cross-account access. The role carries the permissions; the session should carry only the time and scope needed for the task.
For a GitHub Actions workflow, OIDC avoids storing a long-lived AWS access key in the repository. AWS must trust the GitHub identity provider, and the role's trust policy should limit which repository and branch can assume it. The subject claim is case-sensitive, so copy the repository and branch values carefully. The workflow also needs permission to request an identity token.
For local development, EnvManager's documented runtime secret command can pass selected environment values to a process. For example:
envmanager run --only STRIPE_KEY -- npm run seedThe command narrows the values available to that process. Use it for a task that needs one key, rather than loading a full production environment into a developer's shell. EnvManager also centralizes and encrypts environment files, so teams can manage access without pasting secrets into chat or shell history.
A gradual move is often safer than a one-shot replacement. An incremental path works well: first control existing credentials, then shorten their lifetime, and remove stored credentials where the systems allow it.
Milestone: Pick one delivery method and identify how its credential expires. If the method has no clear expiry or revocation path, don't treat it as temporary.
Step 3: Configure Authorization and Deliver the Secret Securely
Authorization decides what an identity can do after it proves who it is. Keep the trust rule and the permission rule separate: one says who may assume access, and the other says what that role can reach.
For an AWS OIDC setup, first add GitHub's OIDC provider in the AWS account. Then create a role that trusts that provider. In the trust policy, restrict the subject claim to the intended repository and branch. Grant the role only the actions and resources needed for the job. Start with read-only access when that is enough, then add a specific write action only if the task requires it.
Store the role identifier in the repository as a variable, not as a secret. It routes the workflow to the role, but it is not a credential. In the job definition, allow identity-token requests and configure the AWS credentials step to assume the role. Run the STS identity check before adding deployment actions.
For human access, require strong sign-in and MFA before granting a sensitive role. If the access is an emergency exception, capture a reason and approval in the same workflow. An access-management system can require approval and record who had access, when it was active, and why it was granted.
Deliver credentials through the platform's secure exchange or inject them at runtime. Don't paste a secret into a ticket, workflow file, or command argument that may show up in logs. For an application that receives a bearer token, use an encrypted connection and make the application validate its issuer, audience, scope, and expiry.
Keep the delivery channel as narrow as the permission. A deployment job should receive its own role session. A developer should not need a shared team key just to run a local seed command. With EnvManager, use the command's --only option to pass only the required value to the child process.
Milestone: The right identity can request access, but unrelated identities and workflows cannot. Keep the reason for any human elevation with its approval record.
Step 4: Test the Scope and Expiration
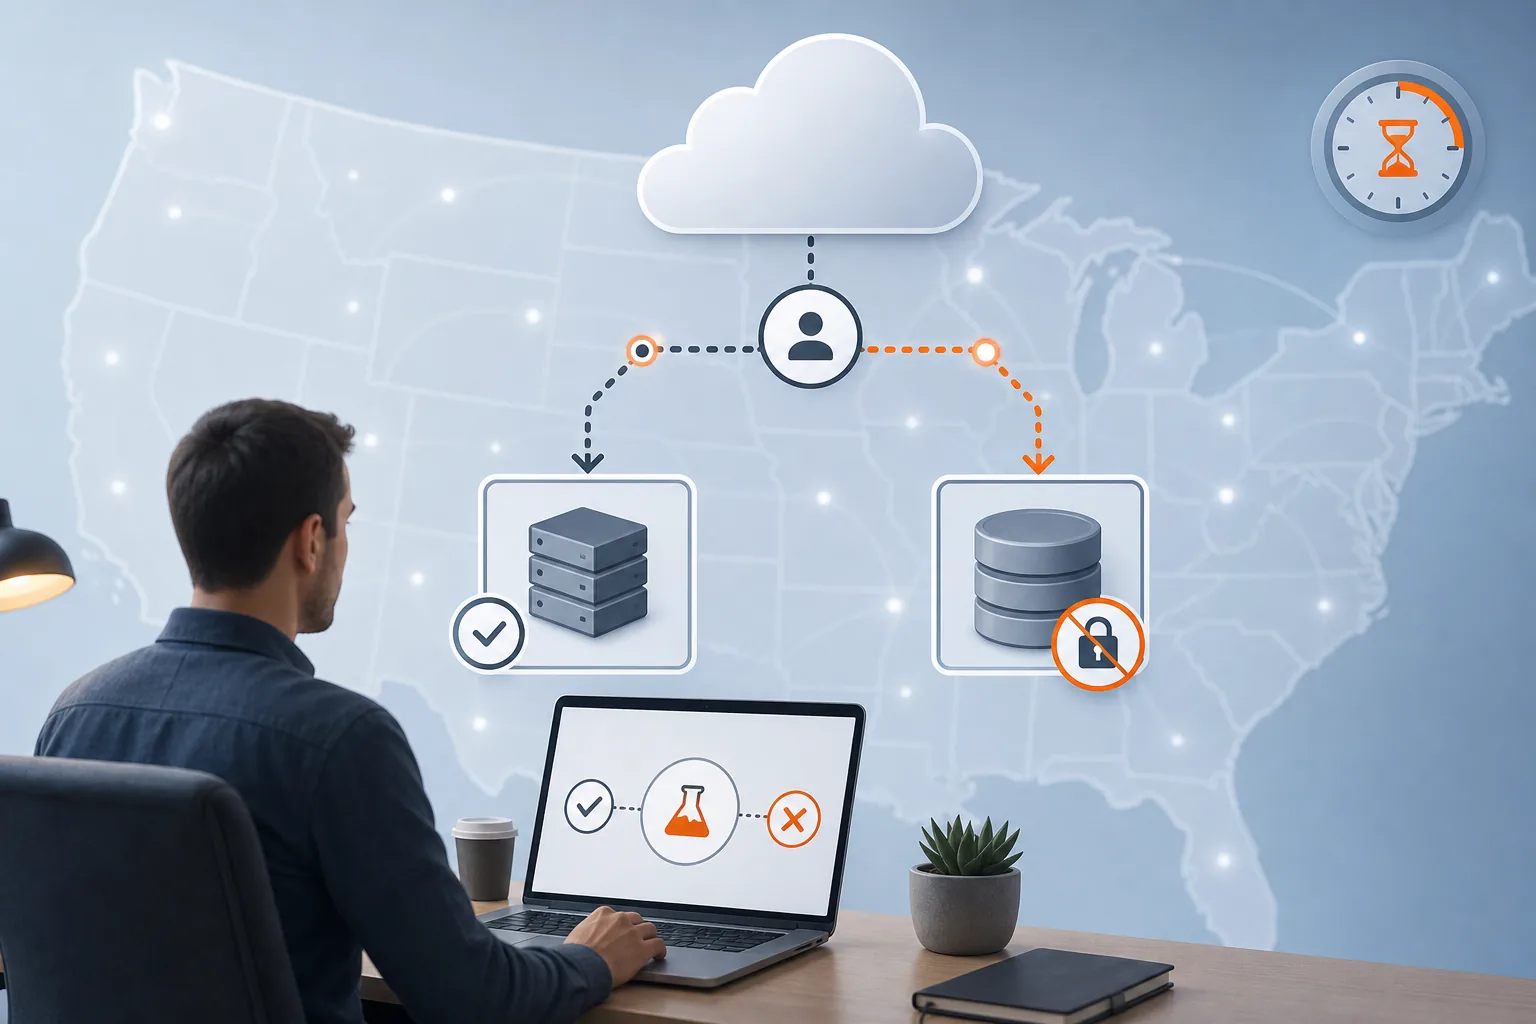
A policy that looks right can still be too broad. Test the allowed path and the denied path with a low-risk task before using the credential on production data.
For a cloud role, run the identity check from the intended workflow. Confirm that the returned identity is the expected assumed role. Then try one permitted read operation. Do not stop at a successful login: authentication proves identity, not that the role has the right boundary.
Next, test a resource that should be outside scope. A job meant to read one project should be denied when it asks for another. A read-only role should fail when it tries to write. Use a harmless test resource so a policy mistake cannot alter live data.
Check time limits too. Record when the credential was issued, then try it after its expiry or after the job ends. It should fail. Some systems distinguish the lifetime of the underlying token from the lifetime of a signed link or session, so verify both if your workflow uses more than one credential type.
For a local command, inspect the child process environment without printing secret values. Confirm the selected variable is present for the task. Check that unrelated secrets are absent. Then close the process and confirm the credential isn't left in a saved file or shell startup setting.
Presigned links need special care. Anyone who gets a bearer link may use its permitted action until the link expires. Test the intended download, then check that an expired link fails. Also test a different object or bucket that should be out of scope. A successful URL creation alone does not prove the signer had only the permissions you intended.
For this check, use synthetic data and a separate test resource. The just-in-time access workflow is useful when the permission should exist only during an approved task and end automatically afterward.
Milestone: Save the result of one allowed request and one denied request. If the denied request succeeds, stop and reduce the policy before deployment.
Step 5: Revoke Access and Review the Audit Trail
Expiration is the safety net. Revocation is the fast stop. End access as soon as the task finishes, even if the credential has time left.
For cloud roles, end the session when the platform supports it. If a token or role grant may still be active, remove the grant or disable the identity path. For a compromised static key, revoke it and rotate the secret at the service that issued it. Removing a key from a repository does not invalidate copies already taken.
For people, remove temporary group membership or role grants after the incident. For CI, disable the workflow permission or trust condition if the repository or branch no longer needs access. When a developer leaves, follow a full offboarding process instead of relying on the short lifetime of one session.
Review the records tied to the grant. At minimum, you want to know which identity requested access, who approved it when approval was needed, what resource it could reach, and when the grant ended. Keep change records distinct from secret values. An audit trail should help explain who changed policy without exposing the credential itself.
For AWS workloads, send relevant access events to your monitoring flow. Event-routing rules can send selected events to an alert or response action. Alert on unexpected role assumptions, denied access spikes, or a workflow using a role from an unexpected branch. Tune alerts to a specific identity or role so normal deployments don't bury the signal.
EnvManager records changes in an immutable audit trail, which gives a team a durable record of secret and access changes. It also supports role-based access for team members. Use those controls alongside the destination system's logs; a secret manager's record cannot replace cloud-side evidence of what a credential did.
If temporary access becomes a recurring exception, fix the normal role or workflow rather than extending each grant. Record the task's owner and remove the exception once the routine path works.
Milestone: Close the grant, confirm it no longer works, and review the related events. Then set an owner and review date for any remaining standing access.
FAQ: Temporary Scoped Secret Access
What is temporary scoped secret access?
Temporary scoped secret access gives a named person or workload limited permission for a defined period or task. The scope can restrict the resource, action, or environment. The credential then expires or gets revoked when the work ends. This reduces the time and reach available to someone who obtains the credential.
How do I get temporary AWS credentials for a CI job?
Use an identity flow such as GitHub Actions OIDC to let AWS verify the workflow, then have the job assume a narrowly scoped IAM role through STS. Limit the trust policy to the intended repository and branch. Give the job only the permissions it needs, and verify the assumed identity before running deployment steps.
How long should a temporary secret last?
Set the lifetime to match the task, not a general team habit. A single job should use credentials that expire with the job when the service supports it. A human session should end after the approved work window. Confirm the actual expiry value rather than assuming a platform default.
How can I check that a secret is truly scoped?
Test both sides of the policy. Make one permitted request, then try a harmless request to a resource or action that should be denied. Check that the secret is available only to the intended process or job. Finally, test after expiry and review the system's access records.
Conclusion
Use identity-based credentials where you can, narrow every grant to one task, and test that expiry and denial both work. Start with one low-risk workflow, remove its long-lived key, and document the result. EnvManager can help teams scope local secrets to a command; begin by applying the same boundary to one development task.