How to Automate Secret Rotation for API Keys
Learn how to automate API key rotation with safe overlap, secure storage, CI/CD updates, validation, monitoring, and a tested rollback plan.
A key that never changes stays useful to an attacker for as long as it remains active. To automate secret rotation for API keys without breaking services, map every consumer first, then rotate in stages with a clear rollback path.
We analyzed 55 comments from YouTube and Reddit about automated API key rotation and found that 22% mentioned expiry notification and scheduling systems.
Automation can handle the handoff, but it can't fix an unknown dependency or a provider that only allows one active key. Build the workflow around those limits.
Step 1: Inventory API Keys, Owners, and Rotation Constraints
Start with the list of credentials, not the rotation script. A working script can still cause an outage if it changes a key that an undocumented job depends on.
For each key, record its owner, purpose, environment, provider, secret store, and every known consumer. Include local development, production services, deployment jobs, scheduled tasks, and serverless functions. Note how each consumer reads the value. A service that reads a secret at startup needs a different rollout from one that fetches it at runtime.
Then check the provider’s key rules. Can two keys work at once? Can an API create and revoke keys? Does creating a replacement invalidate the old key immediately? These answers decide whether you can use a no-downtime overlap or need a maintenance window.
For each key, also set an owner who can approve a change and respond to a failed test. If there’s no clear owner, resolve that before putting rotation on a timer. A short secret rotation checklist for small teams can help you assign that work.
Mark keys that need urgent attention, such as credentials with broad access or keys exposed in a suspected leak. Give each a named owner and a specific recovery path. A risk-based order helps you start with the keys where a failure or misuse would have the greatest effect.
Milestone: You should have a list of keys, owners, consumers, provider limits, and a priority order.
Step 2: Choose a Rotation Mechanism and Secret Store
Pick a setup that can create or receive a new key, store it safely, deliver it to consumers, and confirm that it works. The store and the rotation engine can be separate parts. What matters is that the handoff has an owner and a test at each stage.
A cloud service may make sense when your workloads already rely on that cloud’s access controls. AWS Secrets Manager supports API key rotation via Lambda.
| Approach | Works well when | Check before you commit |
|---|---|---|
| AWS Secrets Manager with a rotation function | Your workloads use AWS and the provider has an API for key changes. | Confirm the function can create, test, and retire keys in the right order. |
| Vault or another secret store with a custom script | You need to orchestrate a provider-specific rotation flow. | Test retries, permissions, and recovery if key creation succeeds but delivery fails. |
| An environment management workflow | You need secrets delivered to apps or build jobs. | Verify what handles rotation itself, and what only stores or syncs values. |
| External Secrets Operator with a Kubernetes reloader | Your Kubernetes workloads need changed values to reach running pods. | Check refresh behavior and whether the app reloads the value or needs a restart. |
| A scheduled or event-triggered script | You can call the provider’s key API and maintain the workflow. | Include safe retries, a validation call, alerts, and a rollback path. |
Tools don’t all mean the same thing by “rotation.” Some create a replacement credential. Others store or sync a value that another system rotates. Confirm which component creates the key, which updates consumers, and which revokes the old value. You can also connect a custom script to a CI/CD or Atlassian workflow, but the workflow still needs access controls and clear failure handling.
EnvManager can serve as the shared, version-controlled place for .env values, with role-based access and sync to local machines and CI/CD pipelines. Use a separate orchestrator or script for key creation and revocation. This division keeps secret distribution clear without treating storage as proof that rotation is automated.
Set the schedule based on your risk policy and what the provider supports. Keep an on-demand trigger for a suspected leak or other security event. Don’t pick an interval just because a tool has a default.
Step 3: Build an Overlap-Safe Rotation Workflow
Use an overlap when the provider supports two active keys. The old key stays valid while consumers receive and test the new one. That avoids a gap where the provider rejects requests before every application has updated.
Build the workflow in this order:
- Create: Ask the provider for a new key. Keep the old one active.
- Store: Write the new value to the approved secret store as a pending version. Keep permissions limited to the rotation job and the consumers that need it.
- Distribute: Trigger a refresh or deploy so applications can read the new version. Don’t put the value in source code, build output, or a ticket.
- Test: Make a real, low-risk request to the provider with the new key. Check the response and the service’s own health signal.
- Promote: Mark the new version as current after the checks pass. Keep the former value available for a defined recovery window.
- Revoke: Remove the old key only after you’ve confirmed consumers use the new one.
For webhook signing secrets, the same overlap idea applies to verification: accept a signature made with either active secret during the transition, if the provider supports that pattern. A hard cut can reject valid events while application instances still hold the old value. The rollout details differ by provider, so test how its keys behave before relying on overlap.
A useful automation state model is pending, tested, current, and retired. Each state change should be recorded with the rotation job and its result. Make each action safe to retry. If a job runs twice after a timeout, it shouldn’t revoke a key that consumers still need.
For a provider-specific example of staging the replacement and checking traffic before revocation, see the Stripe key rotation workflow. Apply the provider’s own rules rather than assuming every API offers the same overlap window.
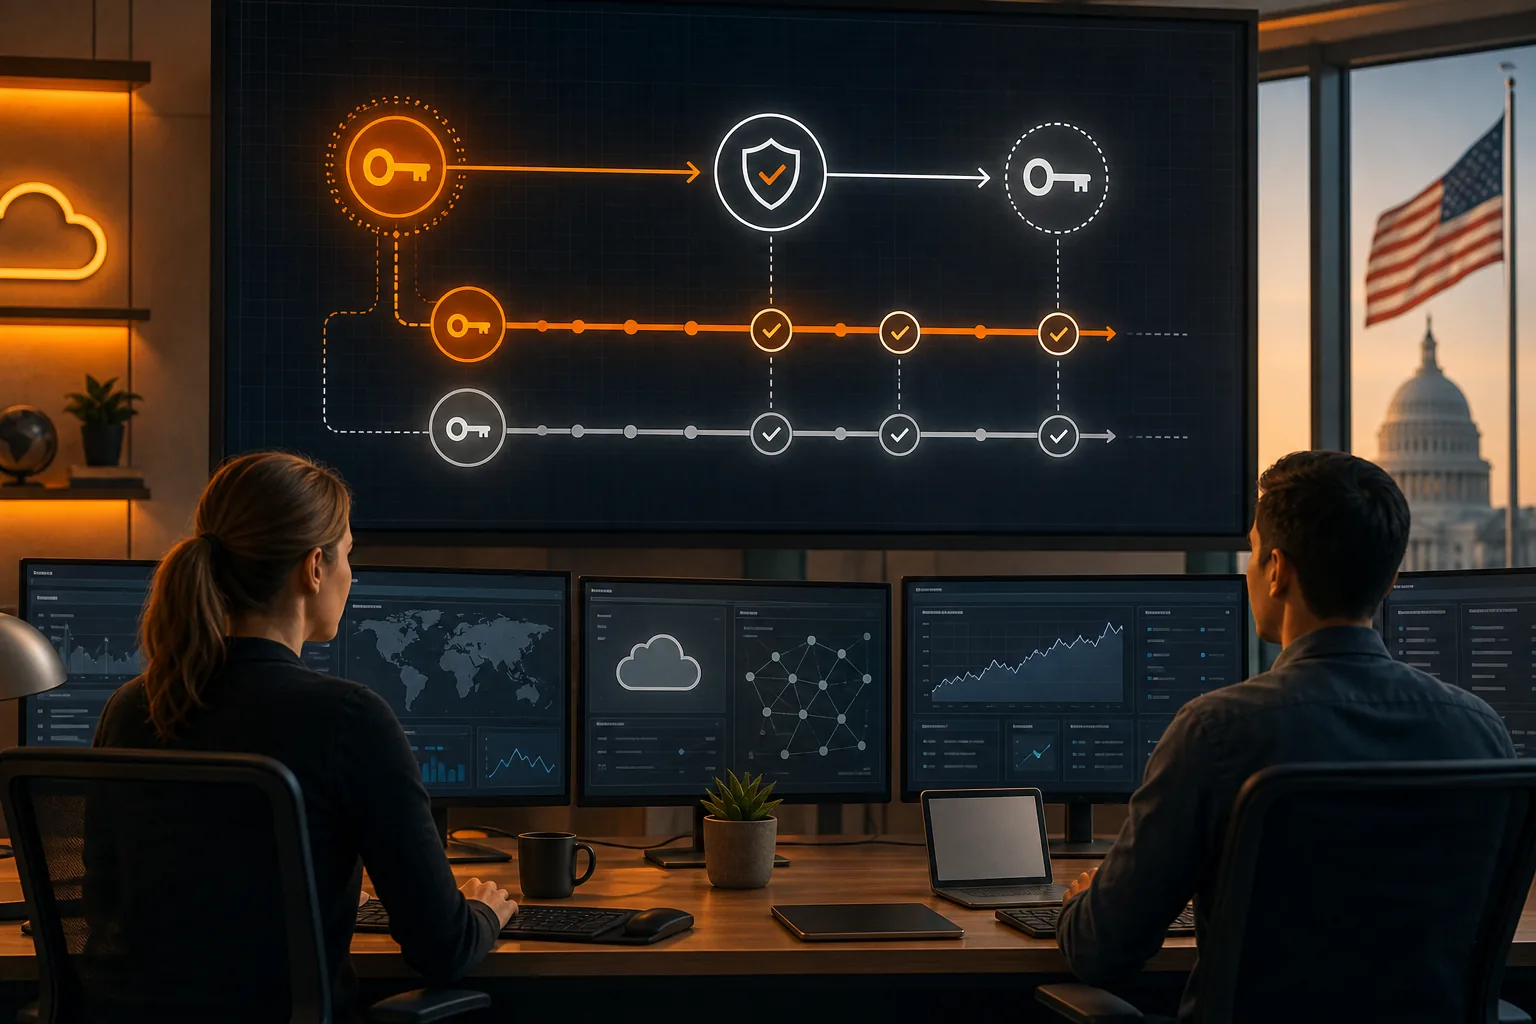
If a provider permits only one active key, don’t pretend the overlap exists. Schedule a short change window, prepare the new value and deployment in advance, and decide how to pause or reroute traffic if validation fails.
Step 4: Distribute the New Key to Applications and CI/CD
Rotation only works when each consumer receives the new value. Prefer runtime retrieval from a central secret store over copying long-lived values into application settings or pipeline files. EnvManager can centrally manage encrypted .env files and sync secrets to local machines and CI/CD pipelines, which can reduce manual copy-and-paste during delivery.
First, group consumers by how they load secrets. An application may read its environment at startup, fetch a value during each run, or hold it in memory. A CI job might need the key only for one build. These patterns determine whether a refresh is enough or the service needs a restart.
For Kubernetes, External Secrets Operator can sync values from a secret store into Kubernetes Secret objects. A reloader can then prompt workloads to respond to a changed value. Check the whole chain: a synced secret doesn’t guarantee that a running process has stopped using its cached value.
For serverless workloads, check when the runtime reads the secret and whether it caches that value between requests. A new version in the store may not affect a warm execution environment immediately. For edge runtimes, use the platform’s secret update path and test propagation in a non-production environment before relying on it.
Keep CI/CD access narrow. Give each job only the secrets it needs, and make the job request them at run time when possible. Mask secret values in logs. Avoid printing environment dumps during debugging, since a successful rotation can still expose the new key through build output.
Store the new value in the source of truth, not in a Git commit. GitOps can track the configuration that points to a secret or its version, while the secret value stays outside the repository. That gives reviewers a record of the change without turning repository history into another copy of the credential.
Use secret management practices for application and CI delivery to review how your team stores and grants access to values. Then test one consumer at a time before expanding the rollout.
Milestone: Every known consumer should fetch or reload the new version, and your deployment path should keep the value out of logs and source control.
Step 5: Test, Monitor, and Recover from Rotation Failures
Test the new key before you revoke the old one. Use a low-risk request that exercises the same permissions the application needs. A key can be valid yet lack the right scope, belong to the wrong environment, or fail for a consumer that still has stale configuration.
Watch both the rotation job and the services that use the key. Track whether key creation succeeded, whether each consumer updated, and whether requests started failing after rollout. Add an alert for a failed rotation or a rise in authentication errors. Keep logs useful, but never log the secret itself.
Keep an audit record for each run. Record who or what started it, which secret reference changed, when each stage completed, which consumers passed validation, and whether the old key was revoked. EnvManager’s role-based access and version control help teams manage access to environment values and review changes; pair those controls with the rotation job’s own run history.
Define recovery steps before turning on the schedule. If a health check fails, stop the rollout and leave the old key active. Restore the last known-good version for consumers that already changed, then investigate the failing test. Don’t automatically revoke the replacement until you know whether it caused the problem or whether an unrelated service failed.
For a provider that invalidates the old key as soon as it creates the new one, the recovery plan must be different. Prepare the deployment first, test the shortest possible cutover in staging, and agree on a maintenance window. If the provider’s behavior makes a safe rollback impossible, treat that as a design constraint, not a detail to discover during an incident.
Use scheduled runs for routine changes and an event-based trigger for suspected exposure. Add an approval gate for a high-impact production credential if your team needs a human check. An approval step should pause the process before the change, not leave a half-rotated key with no owner.
Finally, review failures and near misses. If a service was absent from the inventory, update the owner and consumer map. If a timeout caused duplicate key creation, make the next run idempotent. Those fixes make the next rotation safer than the last.
Frequently Asked Questions
How often should API keys be rotated?
Set the schedule from your security policy, the key’s access, and the provider’s limits. There isn’t one interval that fits every API key. Rotate immediately when exposure is suspected. For routine changes, document the chosen cadence and confirm the process works before applying it to production credentials.
Can I rotate an API key without downtime?
Yes, if the provider allows the old and new keys to work at the same time. Create the replacement, update consumers, test traffic, and revoke the old key only after the rollout succeeds. If only one key can be active, plan a controlled cutover and test the recovery steps first.
Does a secret manager automatically rotate API keys?
Not always. A secret manager may store or sync values while a separate function or script creates and revokes keys with the provider. Check the full workflow, including key creation, consumer updates, validation, and revocation. Confirm which part retries a failed step and which part alerts your team.
What should I monitor during key rotation?
Monitor each stage of the rotation job and the services that use the key. Check for failed provider calls, missed consumer updates, and authentication errors after deployment. Keep a timestamped record of the outcome and the responsible job or operator. Never include the secret value in logs or alerts.
How do I rotate keys used by CI/CD?
Store the key in a protected secret system or masked CI variable, then let the job read it at run time. Replace the value, run a test job, and check the result before revoking the old key. Restrict access to the jobs that need it and make sure build logs don’t print secrets.
Conclusion
Automate the handoff, but keep validation and recovery in the plan. Start with one high-priority key whose owner and consumers are known. Run the full workflow in staging, confirm the new key works, and only then schedule the production rotation.