How to Rotate Stripe API Keys With Zero Downtime
Learn how to rotate Stripe API keys with zero downtime by mapping every consumer, staging a replacement, checking traffic, and revoking the old key safely.
A Stripe key change can break payments if even one worker, deploy job, or app instance still uses the old value. To rotate keys without downtime, map every consumer first, deploy the replacement during an overlap window, and revoke the old key only after you confirm the switch.
We read the 6 highest-ranking pages for rotating Stripe API keys without downtime: howtorotate.com, vibeappscanner.com, darkbot.io, oneuptime.com, a Dev.to walkthrough, and Stripe's own AWS rotation post. None of the 6 told readers to inventory every key consumer first, such as CI/CD jobs, background workers, or serverless functions, before starting a rotation. Only 3 of the 6 described a dual-key overlap window, and just 1 separated webhook signing secrets from API keys. That is the exact gap where a rotation still breaks payments, one uninventoried worker still holding the old key.
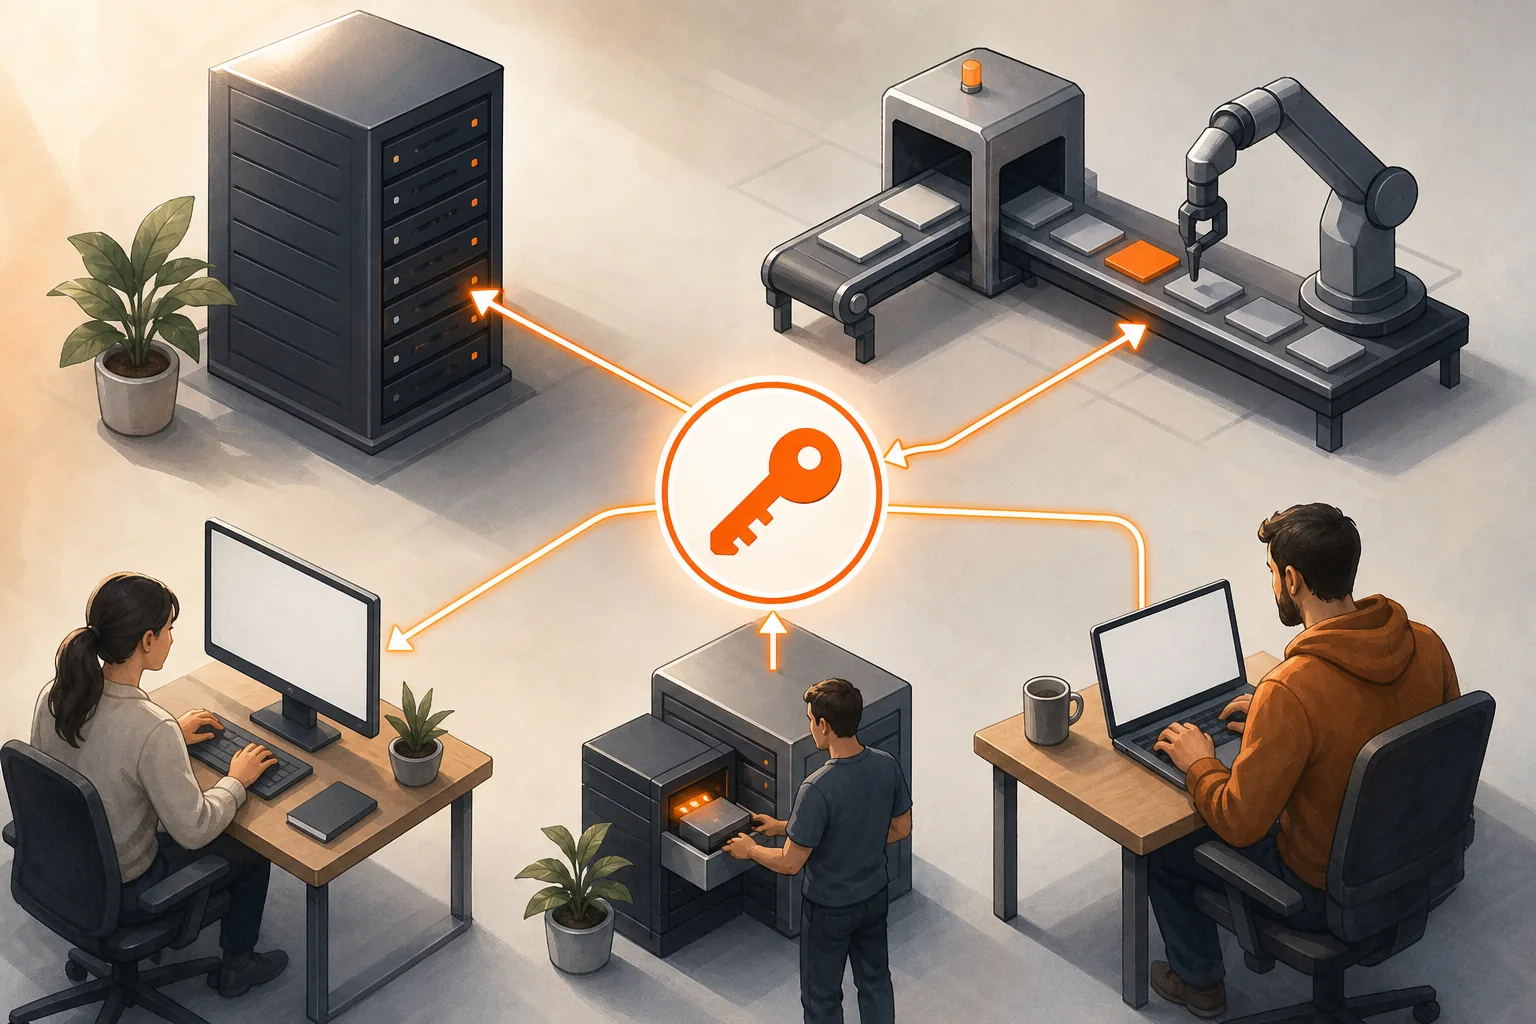
Step 1: Inventory Every Stripe API Key Consumer
The goal is to find every place that sends a Stripe request before you change a credential. Start with the Stripe Dashboard’s API keys page, then check your own systems for copied values and variable names.
Make a short inventory for each key. Record its mode, type, owner, service, and storage location. Keep test and live credentials separate. Test keys start with sk_test_ or rk_test_; live keys start with sk_live_ or rk_live_. Publishable keys use pk_ prefixes and are designed for client-side use.
Search deployment settings and CI/CD variables, then check local development setup, scheduled jobs, background workers, and serverless functions. Don’t stop at the main app. A monthly billing task may run from a separate worker that no one remembers during a release.
Stripe uses keys to authenticate API requests and control which resources a key can access. Webhook signing secrets are separate credentials. Track them too, but don’t treat them as API keys or rotate them as part of this change unless you intend to rotate webhook verification.
Use the inventory to name a technical owner for each consumer. If your team manages environment values centrally, environment-specific variable management can help prevent a test key from landing in production. EnvManager can keep values encrypted and versioned, with access controlled by role.
Mark each consumer as server-side or client-side. Secret and restricted keys must stay on the server; only publishable keys belong in browser or mobile code. API key security practices can help you check for hardcoded values and old copies before you proceed.
By now, you should have a list of services and deploy paths that need the replacement.
Step 2: Prepare a Replacement Key and Secure Distribution
This step gets the new credential ready without putting it in source code or a chat message. For a secret or restricted key, use the Stripe Dashboard for the right account and mode, then store the value in your approved secrets system.
If you’re replacing an unrestricted secret key with a restricted key, first create and test the restricted key in a sandbox. Use successful API calls to work out the permissions it needs.
Test the new key against every service in the inventory. A billing service may need write access to subscriptions, while a reporting job may only need read access. Don’t guess the permissions from the service name. Use request logs and application errors to find missing access before production.
For a like-for-like key rotation, check the Dashboard’s available rotation options and choose a transition window that gives your team time to deploy and verify. Avoid immediate expiration for a planned change unless you’re responding to suspected exposure. Stripe notes that rotating a key creates a replacement ready for use, and that a delayed expiration can provide a rollback window in some cases.
Store the replacement under a clear variable name, such as STRIPE_SECRET_KEY, in your secrets manager or protected environment settings. Don’t paste the actual value into a ticket, build log, or committed .env file. EnvManager helps teams store and version environment values centrally, then sync approved secrets to developers and CI/CD workflows.
Keep the key’s scope visible to its owner. If the replacement is restricted, write down its allowed resources and the service that uses it. This makes a later permission review less of a guessing game.
Milestone: the new key is stored safely, assigned to the right environment, and ready for a test deployment.
Step 3: Deploy Dual-Key Support and Roll Out Gradually
For a zero-downtime cutover, your running services need a controlled path from the old value to the new one. You may not need code changes if your app already reads one key from configuration and can reload or restart safely.
First, confirm how each process reads secrets. Some apps load environment variables only at startup. In that case, changing the value in a vault won’t change the key inside a running process. Plan a rolling restart or deployment so old and new instances don’t all stop at once.
Next, check Stripe’s current rotation flow in the Dashboard. If it allows an overlap period, keep the old key valid while you update consumers. The available settings can change, so use the options shown for the key you’re rotating. Don’t assume every key type has the same rotation behavior.
Update a non-production service first. Deploy the replacement to one instance or a small part of your fleet, then confirm its health checks pass and its Stripe requests succeed. Expand the rollout only after that first group works.
Use the same change path for background workers and scheduled tasks. A web server may be on the new key while a delayed job still holds the old value in memory. Restart workers in a controlled order, and check that queued work continues to run.
For CI/CD, update the protected variable or secret reference used by the deploy job. Make sure the pipeline doesn’t print the value during a build. If your deployment system copies environment values into a release, verify that the next release receives the new version rather than a stale snapshot.
Most teams using a payment-processing library won’t need to change auth code for a key-only swap. Keep the code path stable and change the secret at its source.
Milestone: at least one canary or non-production consumer is making successful requests with the replacement before you widen the rollout.
Step 4: Validate Stripe Requests and Monitor for Errors
Validation proves that the new key works across real application paths, not just in a settings screen. Check both Stripe’s request logs and your own service logs while the overlap window remains open.
Start with the services in your inventory. Run the actions each one normally performs, such as a test-mode payment flow or a read-only report. In production, use safe checks that don’t create unintended charges, refunds, or customer changes.
Watch for authentication errors. Stripe documents that a missing or invalid key can produce an invalid-request error, while a request with an expired key returns an authentication error. A restricted key can also fail when it lacks permission for an operation. Use the request logs to inspect the affected requests.
If a request fails, match the error to the likely cause before changing the key again:
- Authentication failure: Check whether the service loaded the new value and whether it matches the intended test or live mode.
- Permission error: Review the restricted key’s resource permissions, then grant only the access that the failing request needs.
- Only one worker fails: Check whether that process restarted and reloaded its configuration.
- Failures continue after a deploy: Look for another consumer in the inventory that still uses the previous value.
Keep an eye on request success and your normal payment workflow during the rollout. A health check can show that the app is up, but it won’t prove that the billing worker can reach Stripe. EnvManager’s version history can also help you identify which environment value was active during a deployment.
Don’t revoke the old key just because the first test passed. Confirm that every listed consumer has moved and that no stale-key errors appear in the request logs.
Milestone: each known consumer has passed its own request check with the new key.
Step 5: Revoke the Old Key and Confirm Rotation Is Complete
Revoke the old credential only after the rollout is complete and the validation checks pass. For a planned change, use the Dashboard’s rotation or expiration controls and follow the timing shown there.
Before you confirm, review the inventory one more time. Check every app instance, worker, scheduled job, CI/CD variable, and environment. Look for old values in deployment history or local setup notes. Don’t copy the old key into a rollback plan. If a rollback is needed, use the approved replacement and rotation process instead.
When the old key expires, test a normal API request from each critical service. Then review the request logs for authentication failures that point to a stale consumer. If one appears, don’t quietly restore the retired value as a permanent fix. Find the consumer, update it, and confirm that it uses the current key.
For a suspected leak, treat the situation differently. Stripe recommends rotating exposed secret or restricted keys promptly. A long overlap can leave a compromised credential usable, so prioritize stopping unauthorized access and follow your incident response process.
After revocation, remove outdated copies from local files and deployment settings. Keep only the current secret in the approved store. Stripe advises that secret keys stay out of code and recommends storing them in a secrets vault or, where one isn’t available, in environment variables. Avoid exposing secrets through logs or diagnostic pages.
Rotation is complete when all known consumers use the replacement, the old credential is inactive, and your logs show no remaining stale-key requests. Record the owner and completion time so the next change has a clear starting point.
FAQ
Can I rotate a Stripe API key without downtime?
Yes, a planned Stripe API key rotation can avoid downtime when you deploy the replacement while the old key remains valid. Inventory every consumer first, then use the transition option Stripe provides for that key. Restart or reload each service and confirm its requests succeed before the old key expires.
How long should I keep the old Stripe key active?
Keep the old key active only long enough to update and check every consumer. Choose a transition period that fits your deployment and rollback process, using the options shown in the Dashboard. If you suspect the key has leaked, prioritize revocation over a long overlap.
Do I need to rotate Stripe webhook signing secrets too?
No, rotating an API key doesn’t automatically mean you need to change webhook signing secrets. A signing secret verifies incoming webhook events and is separate from an API key. Rotate it only as a separate task, then update the webhook receiver and verify signature checks before retiring its old value.
Can I expire a Stripe publishable key?
Publishable keys are meant for client-side use and don’t grant the same access as secret or restricted keys. Keep publishable keys distinct from server credentials, and handle any publishable-key change using the Dashboard options Stripe provides.
Conclusion
Use an overlap-based rollout for planned Stripe key changes, and revoke the old key only after every consumer passes a request check. Start by building the service inventory, then assign an owner to verify the cutover. EnvManager can help keep the replacement in a controlled, versioned environment rather than scattered across files and deploy settings.