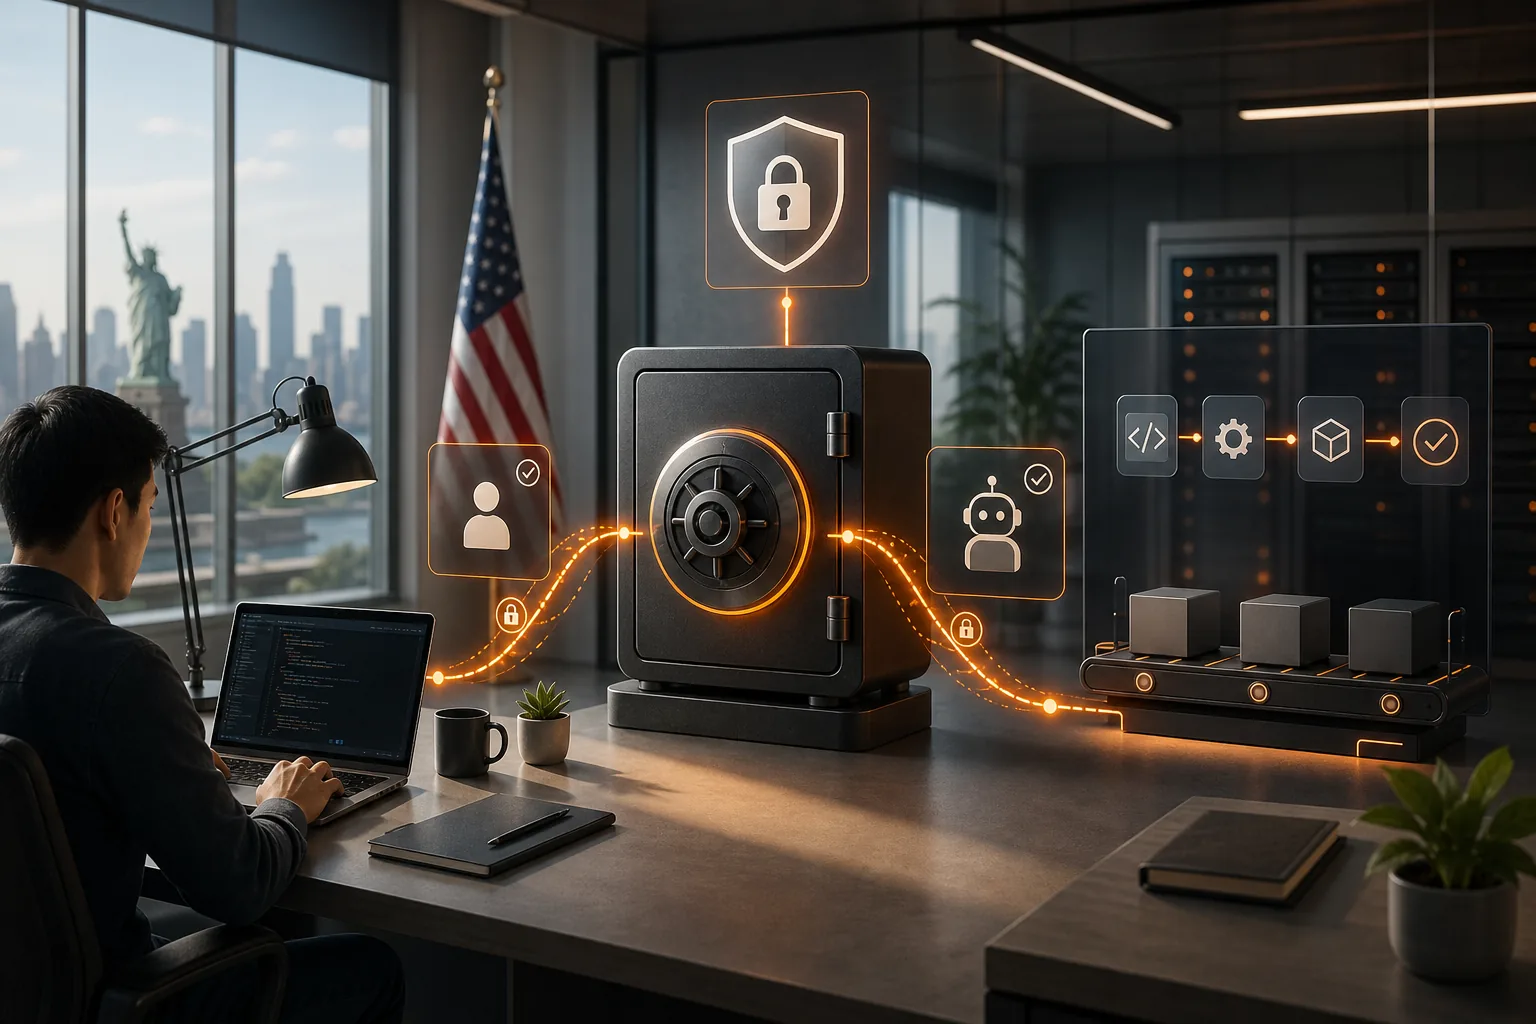
A Secure Workflow for Running Agents With Hidden Secrets
Build a secure workflow for AI agents that need secrets. Scope access, inject credentials at runtime, isolate tools, and track every secret change.
An AI agent can leak a secret without ever being told to. A prompt injection or unsafe tool call may expose credentials the agent can reach. A secure workflow for running agents with hidden secrets keeps each credential scoped, injects it only when needed, and limits what the agent can do with it.
We analyzed 42 comments and questions from Reddit, YouTube and Quora about secure workflows for agents and found that 19% mentioned sandboxed least-privilege execution.
Step 1: Define What the Agent Can Access
Start with the task, not the agent’s wish list. A coding agent that runs tests may need a package registry token. It probably doesn’t need production database access. Give it the smallest set of permissions that lets it finish its assigned work.
Write down the agent’s identity, task, environment, and required systems before you grant access. Treat each agent or workflow as its own identity. Don’t lend it the developer’s personal access token. If the agent acts under a person’s broad permissions, an error or prompt injection can affect everything that person can reach.
Separate development, test, and production credentials. A test job should not inherit a production key just because both jobs run in the same project. For production access, decide who or what can approve the task, and when that access should expire.
Map tools to actions, too. A task that reads an issue may need read access to an issue tracker, but it doesn’t need permission to change billing records. Record those boundaries in a policy or agent configuration, then check that the runtime actually enforces them. EnvManager’s guide to role-based permissions for environment variables can help teams separate access by role and environment.
Keep the list small. Review it whenever the task, tool set, or environment changes. A prompt that says “don’t access production” is guidance to a model, not an access control.
Step 2: Store Secrets Centrally and Scope Access
Move credentials out of prompts, source files, agent memory, and container images. Store each secret in a managed central location, then grant access to the workload that needs it. That makes rotation or revocation possible without editing the agent’s instructions or rebuilding its code.
Keep separate values for each environment. Give a local coding session its development keys, not the same keys used by a release job. Use role-based access control, or RBAC, to decide which people and service identities can read or change values. Pair scoped credentials with infrastructure controls, since app-level rules alone can’t limit what a workload can reach.
EnvManager centrally manages encrypted, version-controlled .env files with role-based access. Teams can sync secrets to local machines and CI/CD pipelines, then keep a record of changes in an immutable audit trail. That gives developers a shared source of truth instead of a trail of copied values in chat and settings pages.
Scope each agent run to the exact keys it needs. If a job needs a payment test key and a database URL, don’t give it every variable in the project. Keep the allowed keys in a reviewed configuration so an agent can’t expand its own access by changing a prompt.
Make access fail closed. If the secret service can’t confirm the agent’s identity or scope, stop the run rather than falling back to a broad local file. Keep a human owner for each production credential, too, so someone knows who should approve changes.
Step 3: Inject Secrets at Runtime, Not Into Prompts
The model needs to use a credential, not read it. Pass the secret to the specific process that needs it when that process starts. Don’t paste the value into a prompt, tool description, chat history, or generated code.
With EnvManager, a command can receive only named variables at runtime. For example, this command gives a seed job access to one key:
envmanager run --only STRIPE_KEY -- npm run seedThe agent can ask to run the command without receiving the key in its conversation. EnvManager’s runtime secret injection command supports scoped variables and scrubs secret values from command output. For a value that must appear in a command argument, use a placeholder rather than typing the secret itself.
Runtime injection reduces accidental exposure. It doesn’t make an untrusted program harmless. A process with access to its environment may still inspect that environment, so only pass it the keys it needs. Don’t use a broad “all secrets” option as the routine path.
Also check what the tool writes. Logs, error messages, shell history, temporary files, and build artifacts can all retain sensitive data. Mask secret values in output, avoid logging full authorization headers, and keep secrets out of files the agent can read later.
Use dedicated, scoped credentials rather than giving an agent the permissions of the person who launched it. That identity boundary matters even when secrets are injected only for a short-lived process.
Test a failed run, too. If the secret service is unavailable or the requested key falls outside the allow-list, the task should stop with a clear error. It should not quietly switch to a developer’s local credentials.
Step 4: Isolate the Agent and Restrict Its Tools
Assume a prompt injection may get through. Put the agent in a separate execution environment so a bad command can’t freely reach the host machine or another agent’s files. Use a hardened container or a stronger sandbox that fits the risk of the task.
Limit network access at the runtime level. Allow the endpoints the workflow needs, then block unknown outbound destinations. This reduces the paths available for data theft or a remote connection if an agent is manipulated.
Restrict file access as well. Let the agent write to its work directory, not system startup files or shared credentials. Be wary of broad shell access and package installs: a tool call that looks like a normal development step can execute code from an untrusted source.
Keep the tool list narrow for each task. A front-end code change doesn’t need database administration tools. Grant high-impact tools only for a specific job, then remove access when the job ends. A review step can help, but a model judging another model’s command shouldn’t be the only barrier.
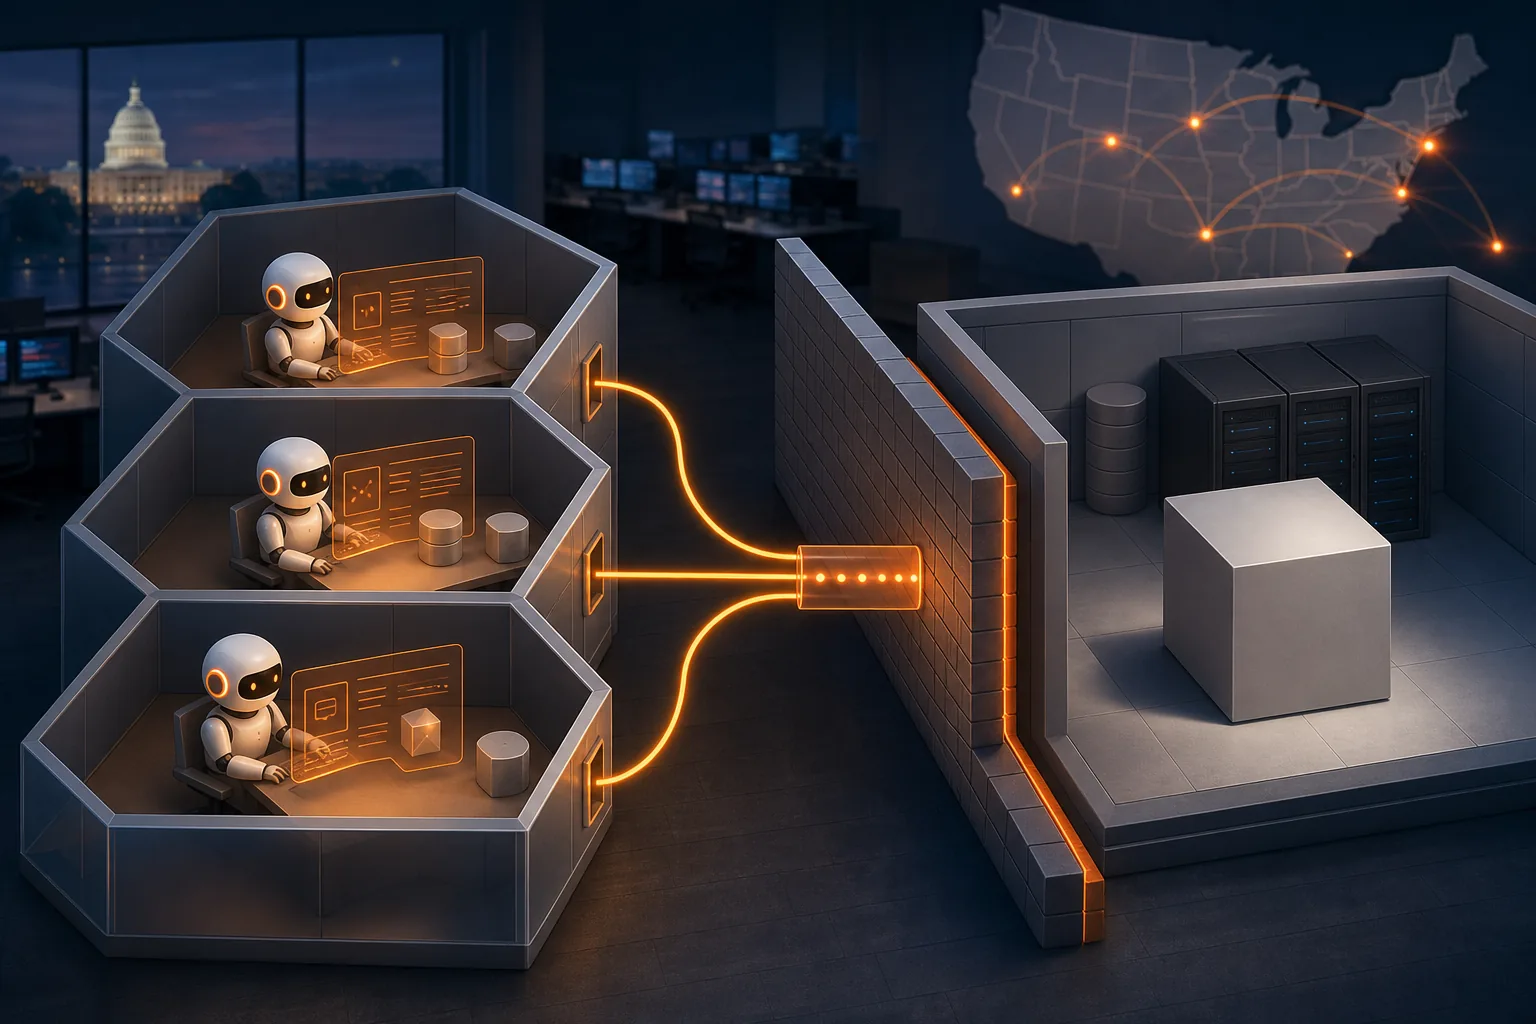
For sensitive workloads, assess whether your infrastructure supports hardware-backed confidential computing, such as a trusted execution environment. Treat it as one layer, not a replacement for access controls or network limits. For shared LLM services, give each tenant a separate identity and secret scope; never rely on the model’s instructions to keep one tenant’s data away from another.
Track tool calls and runtime events so a reviewer can spot a new command, unexpected destination, or unusual access pattern. Static checks can catch hard-coded keys before deployment; runtime checks can flag behavior that changes after a prompt or model update.
Step 5: Audit Access, Rotate Credentials, and Test Recovery
Keep an audit trail that ties secret access and changes to an identity, project, environment, and time. Record enough to answer who changed a value and which workflow used it, but never put the secret itself in the log.
EnvManager versions secret changes and provides an immutable audit trail. That gives a team a way to review changes during an incident or handoff. Pair that record with agent logs that show which tools ran and what resources they requested. The two views answer different questions: the secret audit shows credential activity, while agent logs show task behavior.
Set a rotation plan for each credential. Rotate after suspected exposure, when an owner leaves, or when a service no longer needs the key. Where the credential system supports it, use short-lived tokens. Keep an owner responsible for the change and confirm dependent jobs can use the replacement before retiring the old value.
Practice revocation. Disable a test credential and confirm the agent run fails without falling back to another account or local .env file. Then restore access through the approved path. For teams building this process, EnvManager’s secrets workflow for AI agents describes scoped runs that keep the value out of the agent’s output.
Turn the rules into checks where you can. A deployment can fail if a production key is present in a development job, if a secret is found in a changed file, or if the agent requests a tool outside its policy. Map checks to your security and compliance requirements, such as SOC 2 controls, and keep evidence of who approved an exception.
Finally, rehearse recovery. Revoke one credential, inspect the audit trail, rotate the value, and rerun the affected workflow. If that process depends on someone remembering a manual step, write down the owner and automate the parts you can.
FAQ
How do you keep AI agents from seeing API keys?
Give the agent a way to use a key without placing its value in the prompt or chat. Store the key centrally, scope access to the agent’s task, then inject it only into the process that needs it. Mask output and limit which variables the process receives. Remember that runtime injection reduces accidental exposure but doesn’t stop a hostile program from inspecting its own environment.
Are environment variables safe for AI agents?
Environment variables can work for a process that needs a credential, but they aren’t a complete security boundary. A command-capable agent may be able to inspect its process environment. Use a central secret manager, inject only the required values at runtime, and run the agent in an isolated environment. Don’t place secrets in prompts or baked-in container settings.
How does prompt injection expose secrets?
A prompt injection can try to make an agent read a file, call a tool, or send data somewhere the task doesn’t require. If the agent can access broad credentials, a successful manipulation may expose them through output or network traffic. Reduce the impact with narrow credentials, restricted tools, controlled network access, and monitoring.
Should an AI agent use my personal access token?
No. Give the agent a dedicated identity with permissions limited to its task. A personal token may carry access the agent doesn’t need, and actions can be harder to separate from your own. A scoped identity makes it easier to review activity, revoke access, and change the agent’s permissions without changing your account.
What should you audit when an agent uses secrets?
Record which identity requested access, which environment it used, and when the access or secret change occurred. Also log the tools and resources used during the run. Keep secret values out of logs. Test that you can trace a credential change to its owner and connect an agent’s activity to the workflow that started it.
Conclusion
Keep credentials out of agent context, give each run only the keys it needs, and enforce limits outside the model. Start by scoping one agent workflow with EnvManager, then test that it can complete its task without reading or printing the secret.