Best Environment Variables vs Config Files
Compare environment variables vs config files for security, portability, and team workflows, including .env, config.json, and EnvManager.
A plain .env file is easy to start with. It can also become a secret leak, a stale deploy, or a guessing game during an incident. Here are the five strongest choices for environment variables vs config files, with the right fit, trade-offs, and next move for each.
1. EnvManager
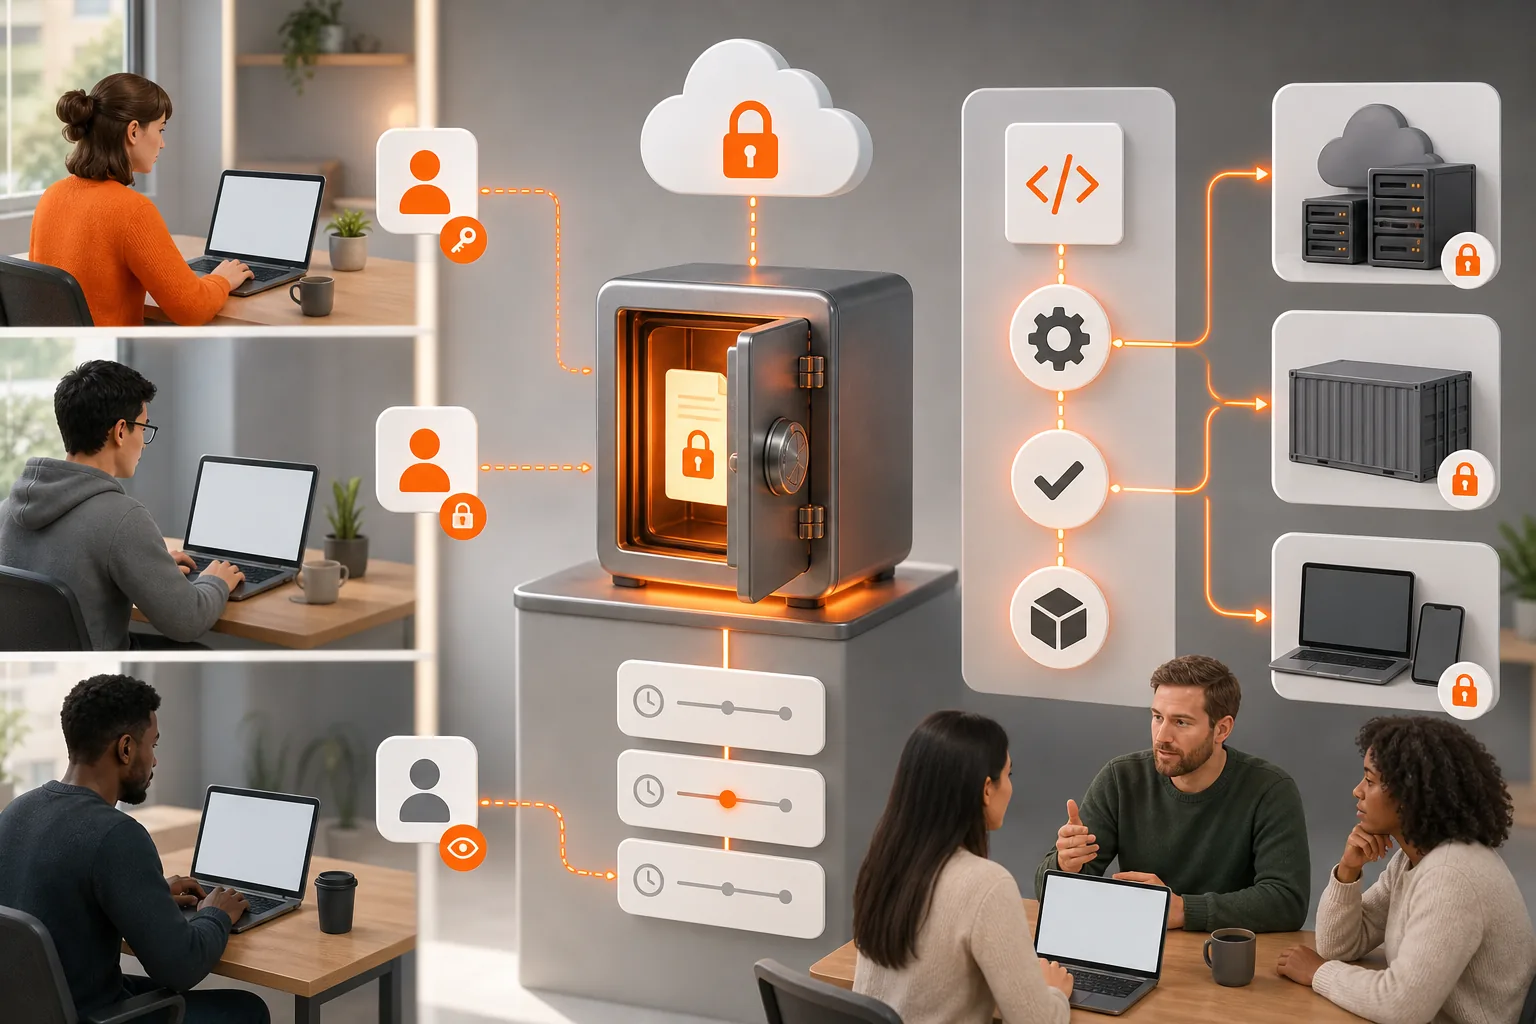
EnvManager is a self-serve service for teams that need shared, controlled environment values. It is a strong fit for DevOps teams, SaaS developers, and security leads who manage secrets across local machines and CI/CD.
We encrypt every value with AES-256 on import. That means the stored secret is protected at rest, rather than sitting in a readable file on one developer's laptop. EnvManager also keeps versions of your environment data, so you can trace a change or restore a known-good set.
RBAC, or role-based access control, lets you give people access based on their job. A developer may need development values. A release lead may need production access. Those permissions don't have to be the same.
The workflow also removes copy-pasting. You can sync approved values to local machines and CI/CD pipelines instead of passing secrets through chat or shared documents. Teams comparing environment variables vs config files often need this control layer more than they need another file format.
EnvManager's own site is the clearest source for its encrypted secret storage and access controls. Audit-log details still need direct verification for your own compliance needs.
Start with one service. Move its local and deployment values into a shared environment, then test the pull and release flow before migrating the rest.
Teams that need separate values for development, staging, and production can use environment variable management across environments as the next design step.
| Need | EnvManager fit | What to check |
|---|---|---|
| Keep secrets out of plain files | Strong fit | Confirm encryption and key-handling needs |
| Share values across a team | Strong fit | Set roles by environment |
| Sync with CI/CD | Strong fit | Test the pipeline pull flow |
| Review past changes | Good fit | Define who can restore versions |
2. Environment Variables, Best for Runtime and Deployment Settings
Environment variables are values supplied to a process at runtime. They are a good fit for deployment settings that change by host, stage, or execution context.
A service might read a database host fromDATABASE_HOST. A CI job might inject a token only while the job runs. This keeps sensitive values out of application code and can prevent credentials from entering a Git repository.
But environment variables aren't automatically safe. A process can read them. A dependency can read them too. Debug output, crash reports, shell history, or an overly broad process inspection command can expose them.
The right question in environment variables vs config files is often about the threat you face. Variables reduce the chance of committing a secret by mistake. They don't protect a running process that already has access to the secret.
The standard definition of environment variables describes them as dynamic values that affect running processes. That explains their strength and limit: they belong to the process context, not to a full permission system.
Use environment variables for deployment-specific values. Keep harmless defaults in code or a checked-in config file. Put secrets behind a managed system when several people or pipelines need them.
Python teams should also decide how missing values behave. Python environment variable access with os.environ and os.getenv explains the difference between failing on a missing value and returning a fallback.
3. Config Files, Best for Structured, Reviewable Application Settings
Config files are best for structured settings that need clear names, nested data, comments, or review by the team. They work well for application behavior that isn't secret.
A config file can group related values in one place. It can describe feature flags, service endpoints, retry rules, or display settings. That structure is easier to inspect than a long list of shell exports.
Config files also make local setup easier when every developer needs the same safe defaults. A checked-in example file can show the expected shape without exposing a real password. The private copy belongs outside version control.
Security depends on the contents and location. A plain file with a production password is still a plain file. File permissions help, but they don't provide the same shared access model as a dedicated secret manager.
Community discussion on storing passwords as variables or files points to the same trade-off: both approaches can fail after a system compromise. Environment variables may help avoid accidental commits, while a file can provide tighter local file permissions. The right choice depends on who can access the host and how the application loads the value.
That makes config files a good home for public or low-risk settings. It makes them a poor default for credentials that many people need across several environments.
Use a sample file such asconfig.example.jsonto document required keys. Keep the live file ignored by Git, and add a startup check that fails before deployment when a required secret is absent.
4. .env File, Best for Local Development Defaults
A .env file is a simple text file that holds key-value pairs for local development. It is the best fit for a small project where each developer needs a private set of local values.
A common pattern looks like this:
APP_MODE=development
DATABASE_URL=postgres://localhost/app
API_TOKEN=replace-me
A local environment-file mechanism reads the file and places those values into the process environment. The code can then use the same variable names in local work and in deployment.
The weak point is the file itself. It can be copied, attached to a ticket, backed up, or committed by mistake. Adding.envto.gitignorehelps, but it depends on every contributor remembering the rule.
Never treat a .env file as encrypted storage. Use a safe example file with placeholder values. Keep real secrets out of pull requests, screenshots, logs, and shell commands.
The dotenv approach is still useful because it keeps local setup fast. A new developer can copy the example, fill in local values, and run the service without changing source code. That convenience is why .env files remain common in the environment variables vs config files debate.
For Linux teams, Linux environment variable setup with export and .bashrc helps separate shell behavior from application configuration. That distinction matters when one terminal sees a value and another does not.
Use .env for local defaults. Move shared or sensitive values into EnvManager when the team starts repeating the same manual setup.
5. config.json, Best for Explicit JSON-Based Configuration
config.json is a clear choice when your application already expects JSON and needs nested, typed settings. It suits services with a stable configuration shape and a strong need for readable structure.
For example:
{ "server": { "port": 8080, "debug": false }, "features": { "newCheckout": true }
}
JSON makes the shape visible. A reviewer can see which values belong to the server and which belong to a feature. Many languages also have built-in JSON parsers, so the loading step is easy to test.
That clarity comes with limits. Standard JSON doesn't allow comments. Secrets placed in the file are exposed to anyone who can read it. A checked-in production file can also reveal infrastructure details that developers don't need.
A safer pattern keepsconfig.jsonfor non-secret settings. Load sensitive overrides through the runtime environment or a secret manager. Validate both sources at startup so a missing value fails early.
Teams building an app template with pre-wired analytics and API keys face the same boundary. A project template can put those keys on the app's configuration surface, which still leaves you responsible for where private values live.
Choose config.json when structure and review matter more than secret storage. Pair it with a separate secret path instead of turning one file into a catch-all.
FAQ
Are environment variables safer than config files?
Environment variables can be safer against accidental Git commits, but they aren't automatically secure. A running process and its dependencies may read them. Config files can have tighter file permissions, yet plain secrets remain exposed on disk. For environment variables vs config files, choose based on your threat model, then add managed access for shared secrets.
Should secrets go in a .env file?
Secrets can live in a .env file for local testing, but a .env file shouldn't be your shared production store. Keep it out of version control and use placeholders in the example file. When several developers or CI jobs need the same values, use EnvManager or another managed secret system.
When should I use a config file instead of environment variables?
Use a config file for structured, low-risk settings that benefit from review. Use environment variables for values that change by runtime or deployment stage. In the environment variables vs config files choice, many teams use both: config files hold safe defaults while a managed system supplies secrets.
Can config.json store passwords securely?
Config.json does not secure passwords by itself. JSON only defines the data format. File permissions, encryption, access rules, and secret rotation must come from other controls. Keep passwords outside the checked-in file, load them at runtime, and test that logs never print their values.
What is the best option for CI/CD secrets?
EnvManager is a strong fit in this shortlist for teams that need encrypted storage, version control support, and role-based access. Environment variables can still carry values into a job, but they don't provide the full control layer alone. Start with one pipeline and confirm access, rollback, and failure behavior.
Conclusion
Use config files for safe, structured settings and .env files for small local setups. Use runtime variables for deployment-specific values. When secrets cross team or CI/CD boundaries, choose EnvManager, then migrate one service and run a full pull, deploy, and rollback test.