How to Build an Audit Log for Environment Changes
Build an audit log for environment variable changes that records who changed what and when, limits access, protects records, and ties changes to deployments.
When a production setting changes, a missing record turns a quick check into guesswork. Build an audit trail that ties each change to a person or service, a time, and the affected environment, while keeping secret values out of the log.
Start with the variables that carry the most risk. Then choose one source of truth, control who can write to it, and test that you can trace a change through deployment.
Step 1: Define which environment variable changes to audit
A useful audit log for environment variable changes starts with a clear scope. Decide which actions need a record before you pick a logging method. Otherwise, you may capture too little to investigate a change, or create noisy records that nobody checks.
List the actions your team needs to trace. At a minimum, include creating, editing, deleting, importing, and syncing variables. Add access changes, such as granting a role that can edit production values. If your system records secret reads or reveals, include those events too. A person viewing a secret can matter as much as a person changing it.
Separate values by environment. A staging key and a production key may use the same variable name, but they have different impact. Record the project and environment with each event. That detail helps you avoid confusing a safe test change with a live system change.
Set a rule for sensitive values. The log should record that a secret changed, but it should not print the secret itself. For ordinary, non-secret settings, decide whether your team needs the old and new values or only a version reference. Keep that choice consistent.
EnvManager centrally manages and version-controls .env files, with role-based access and sync to local machines or CI/CD pipelines. Its guide to working with secrets explains why sensitive values need extra care when people view or update them.
Write a short scope list before changing your workflow. Include the event types, environments, and secret-handling rule. That becomes the test plan for the rest of the setup.
Step 2: Choose a source of truth and record each change
Every change needs one authoritative record. If edits happen in a shared .env file, a dashboard, and CI settings without a clear owner, the audit trail can miss the actual change or show conflicting values.
Choose where each variable is managed. For a team that uses several environments, a central manager can keep values and access rules in one place, then sync approved settings to developer machines and deployment pipelines. EnvManager is built for centrally managing .env files with version control and role-based access.
Decide what an event must contain. A useful record answers who acted, what action took place, when it happened, and which project or environment was affected. Include the result, such as success or denial. For a value update, use a version ID or protected before-and-after details. Never place a live secret in a plain-text log.
The EnvManager audit and compliance overview describes records for variable changes, access, and sync activity. Those event types help teams connect a configuration edit to the person and environment involved, rather than relying on chat history.
Use a consistent event format. For example, a record could say that a named user updated DATABASE_URL in staging at a specific time. Keep the key name, but mask the value. If a value must be compared during an investigation, store the versions in a controlled system and link the audit event to the version.
Also decide how automated changes appear. A CI job should have its own identity, rather than borrowing a developer's account. If a pipeline changes a value, the log should make it clear that a service identity acted and identify the job or deployment where possible.
Step 3: Restrict access and protect audit records
An audit log only helps if people cannot quietly alter or erase it. Limit write access to environment variables and make audit records harder to change than the settings they describe.
Use role-based access control, or RBAC, to assign permissions by job. For example, a developer may edit development values but only view production settings. A release owner may approve a production change. Keep administrative rights limited to people who need them, and review access when someone changes teams or leaves.
EnvManager uses RBAC to manage team access to environment files. That gives you a way to separate who can view values from who can change them. The access control checklist also covers least privilege and reviewing permissions as team responsibilities change.
Protect the log itself. Give log readers access to investigate events, but do not automatically give them permission to edit or delete records. If you send events to a separate storage system, restrict its write path and retain an independent copy. Those controls help preserve the record if an account with broad permissions is misused.
Restrict environment-variable changes to authorized users and processes, then audit those changes. Limit which programs can alter a variable where possible.
Set a retention rule based on your security needs and any requirements that apply to your organization. Don't assume a product keeps audit records for a specific period unless its documentation says so. Check export options as well. If the log stays only in the system being investigated, you may lose access when that system is down or compromised.
For high-risk settings, use a second person to approve changes when your workflow supports it. Keep emergency access possible, but record when it is used and review it afterward.
Step 4: Connect change tracking to deployments and notifications
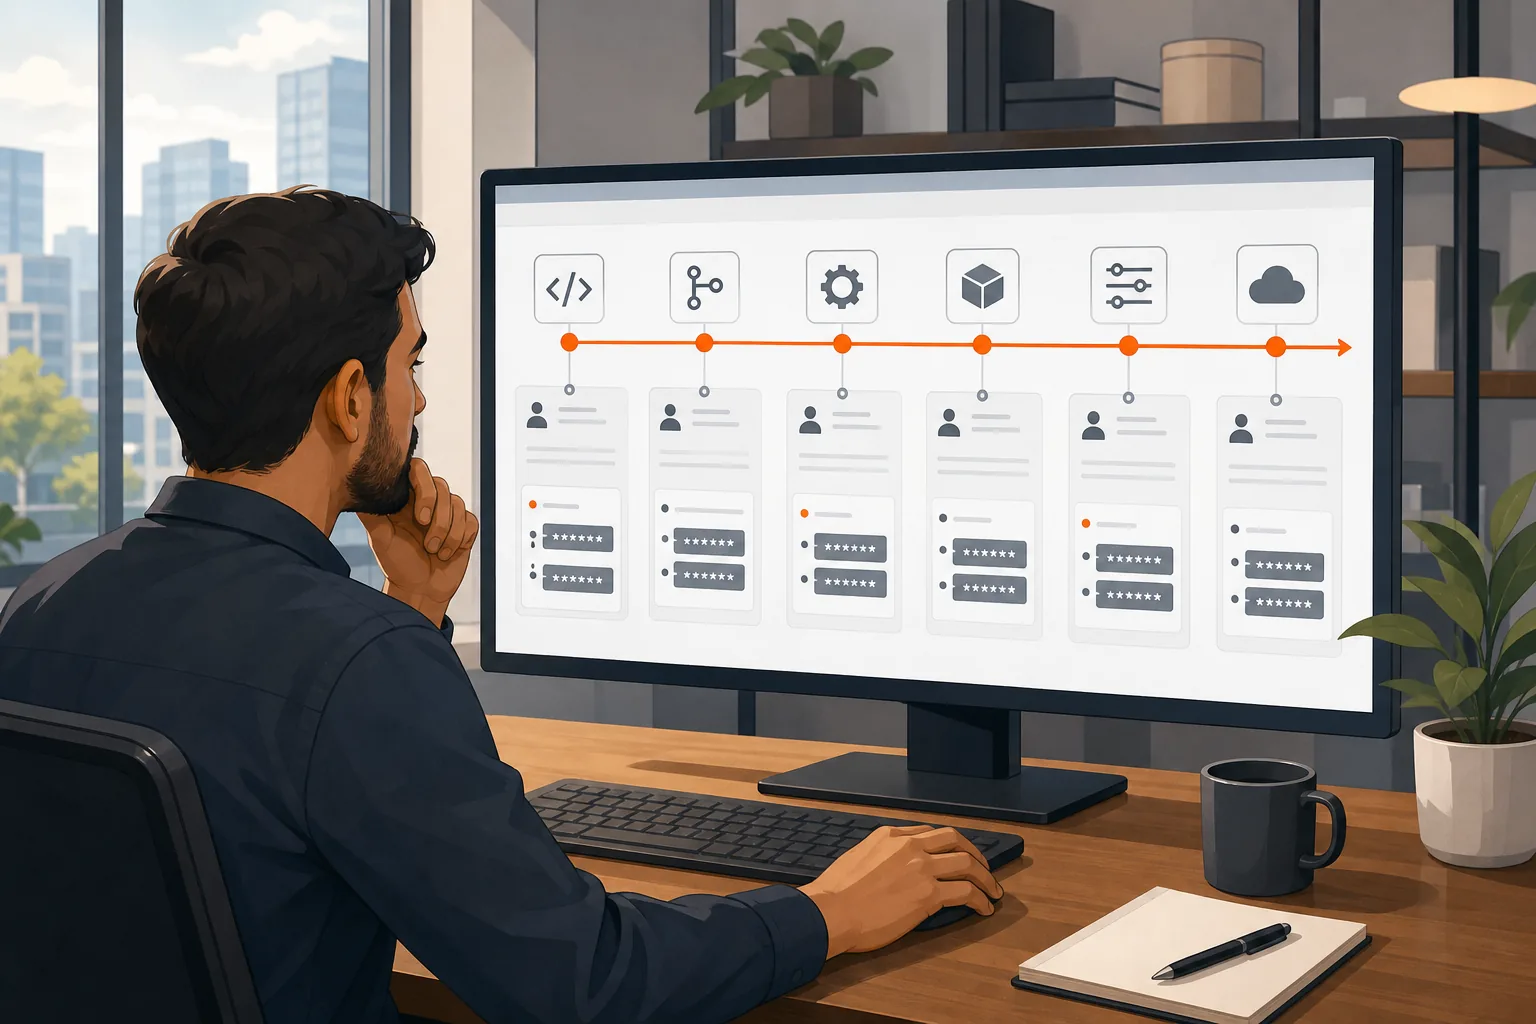
A configuration change becomes easier to investigate when its audit entry connects to the deployment that used it. Record a deployment ID, commit reference, job name, or other stable link alongside the variable-change event when your systems allow it.
Map the path from edit to runtime. A developer may update a value in a central store, then a CI job may pull it during a release. The audit trail should show the human edit and the automated sync as separate events. That distinction helps you find where a bad value entered the process.
Keep environments distinct in the pipeline. A staging job should request staging values, and the production job should use production values only after the required approval. EnvManager can sync centrally managed environment variables to local machines and CI/CD pipelines, so teams can avoid manual copy-and-paste between those steps.
For example, a deployment workflow might run envmanager pull --environment=staging before tests. Treat the command as one part of the record, not the whole audit trail. Capture which identity ran it and which deployment consumed the values.
Notifications can help, but alert only on events someone can act on. Consider alerts for a production secret change, a permission increase, or a failed attempt to edit a protected variable. Include the event and the environment in the notice. Do not include the secret value.
A deployment platform’s environment-variable workflow should make managed variables traceable across deployment steps. Whatever your hosting setup, verify that a change event and its related release can be found without searching through unrelated application logs.
Set a simple response path for an alert: who checks it, how they confirm the change was expected, and where they record the outcome. A notification that nobody owns is just more noise.
Step 5: Test the audit trail and review changes regularly
Test the audit trail before you depend on it during an incident. Create a safe change in a non-production environment, then trace the record from the edit through any sync or deployment it triggers.
Check the key details one by one. Can you identify the actor? Does the timestamp include a time zone? Does the entry name the variable and environment? Can you tell whether the action succeeded? Confirm the record does not reveal a secret value in its fields, exports, or notifications.
Then test the edges. Try a denied edit with an account that should not have access. Make a change through the normal CI path. Delete a test variable if deletion is in scope. These checks reveal whether the log covers only dashboard edits or also captures activity through automation.
Audit logs can have different entry types and access rules. Check whether records include fields such as actor, subject, action, and timestamp, and whether access depends on a reader role. Use those as useful questions when checking your own event records, not as assumptions about your system.
Review a small time window on a regular schedule. Look for changes that lack an owner, production edits outside the expected release path, or repeated denied actions. Compare variable events with deployment records when the timing is unclear.
Also test the log’s own safeguards. Confirm the right people can read and export records. Check that ordinary operators cannot erase the history they may need to explain. If you forward events to another system, test that a sample event arrives with its fields intact.
Record what the test found, then fix gaps before broadening use. Repeat the test after changing permissions, deployment steps, or the source of truth.
FAQ: Audit Logs for Environment Variable Changes
What should an environment variable audit log record?
It should record who acted, what changed, when it happened, and which project or environment was affected. Include whether the action succeeded. For secret values, log the variable name and a version reference or protected change detail, not the value itself. Also record automated activity under a service identity so it isn't mistaken for a human edit.
Should audit logs include secret values?
No, an audit log should not expose the live secret value. Record that the secret changed and link the event to a protected version or controlled secret store. This gives an investigator a way to trace the update without copying credentials into a log that may have broader access or longer retention.
How often should teams review environment variable changes?
Review high-risk changes as they happen when your system can alert on them, then check recent activity on a regular schedule. Set the schedule to match your release pace and risk. Review production changes sooner than routine development edits, and investigate changes with no clear owner or deployment link.
Can CI/CD changes be included in an audit log?
Yes, if the variable manager or deployment workflow records automated actions with a distinct service identity. Connect the event to the job or release when possible. This lets you tell a developer edit from a pipeline sync and trace which deployment received the configuration.
Conclusion
Build the log around identity, action, time, and environment, then keep secret values out of its records. Start by testing one non-production variable change from edit through deployment. If the trail is complete and protected, extend the same workflow to higher-risk settings.